
Practise API Design one question at a time. Answer out loud or in writing, get graded, and see exactly what you missed.
What is REST and what are its core principles?
REST (Representational State Transfer) is an architectural style for distributed systems, defined by Roy Fielding in 2000. It is a set of constraints, not a protocol or a standard.
Six constraints define the style:
- Client-server: the two sides evolve on their own.
- Stateless: each request carries everything the server needs.
- Cacheable: responses must say if they can be stored and reused.
- Uniform interface: one consistent way to address and act on resources.
- Layered system: a client cannot tell if it talks to the origin server.
- Code on demand (optional): the server may send runnable code, like JavaScript.
Every request stands alone, as this one does:
GET /articles/42 HTTP/1.1
Host: api.example.com
Authorization: Bearer <token>
Accept: application/json
Statelessness is the main trade-off. Any server node can handle any request, but each call must resend auth and context.
Missed:
Get your own answers graded
Sign up free. Your account comes with 50 credits for grading, and it remembers what you missed.
What it covers
- REST and resource design
- HTTP methods, status codes and errors
- Collections and payload design
- Authentication and authorization
- API security and rate limiting
- Versioning and compatibility
- API styles and real-time delivery
- gRPC fundamentals
- Performance, reliability and observability
- Testing, documentation and developer experience
- Scale and distributed systems
- gRPC in production
All 110 questions
- What is REST and what are its core principles?
- Explain the concept of resources in REST API design.
- Explain the difference between PUT and POST methods.
- What are the most important HTTP status codes for APIs?
- What is the difference between authentication and authorization?
- How do you handle validation errors in APIs?
- What is CORS and how do you handle it in APIs?
- What are the main HTTP methods used in REST APIs and their purposes?
- What are HTTP status codes and give examples of common ones?
- What makes an API RESTful?
- What is the difference between URI, URL, and URN?
- What are query parameters and path parameters? Pro
- What is JSON and why is it commonly used in REST APIs? Pro
- What is Content-Type header and why is it important? Pro
- What are Protocol Buffers and why does gRPC use them?
- How does gRPC differ from REST APIs?
- What are the main advantages of using HTTP/2 in gRPC?
- What types of service methods does gRPC support?
- How do you define a gRPC service in a .proto file? Pro
- What is code generation in gRPC and why is it important? Pro
- What is a gRPC client stub? Pro
- What is the difference between REST and SOAP?
- What is HATEOAS and why is it important?
- When would you use PATCH vs PUT?
- Explain idempotency in API design. Pro
- Compare different API authentication methods. Pro
- How would you implement role-based access control (RBAC) in an API? Pro
- What are the different API versioning strategies? Pro
- When should you introduce a new API version? Pro
- How should you structure error responses in APIs? Pro
- How do you implement pagination in APIs? Pro
- What caching strategies can you apply to APIs? Pro
- How do you implement rate limiting in APIs? Pro
- What are common API security vulnerabilities? Pro
- How do you secure API endpoints? Pro
- How do you implement API key management? Pro
- What is an API Gateway and when would you use one? Pro
- Explain the difference between synchronous and asynchronous APIs. Pro
- How do you design APIs for mobile applications? Pro
- What are webhooks and how do you implement them? Pro
- How do you handle file uploads in APIs? Pro
- Compare REST vs GraphQL APIs. Pro
- How do you handle API documentation and ensure it stays up-to-date? Pro
- How do you implement API analytics and usage tracking? Pro
- What are API design anti-patterns to avoid? Pro
- How do you implement API testing strategies? Pro
- How do you design filtering, sorting, and search on a collection endpoint? Pro
- How should an API client retry a failed request without making the outage worse? Pro
- How would you push real-time updates to API clients? Compare polling, long polling, Server-Sent Events, and WebSockets. Pro
- What is idempotency in REST APIs and which HTTP methods are idempotent? Pro
- What are the different types of API authentication methods? Pro
- What is content negotiation in REST APIs? Pro
- How do you handle errors in REST APIs? Pro
- What are HTTP response headers commonly used in REST APIs? Pro
- What is rate limiting and how is it implemented? Pro
- What is pagination and what are different pagination techniques? Pro
- What is CORS and how does it affect REST APIs? Pro
- What are the considerations for API deprecation? Pro
- How do you implement search functionality in REST APIs? Pro
- What are the differences between API-first and code-first approaches? Pro
- How do you implement real-time features with REST APIs? Pro
- What are the security headers important for REST APIs? Pro
- How do you handle errors in gRPC? Pro
- What is gRPC metadata and how is it used? Pro
- What are gRPC interceptors and what are they used for? Pro
- How do timeouts and deadlines work in gRPC? Pro
- What is connection pooling in gRPC and how does it work? Pro
- How do you implement authentication in gRPC? Pro
- What are the different load balancing strategies in gRPC? Pro
- How do you handle streaming in gRPC? Pro
- What is gRPC health checking and how do you implement it? Pro
- How do you model a non-CRUD action, like cancelling an order, in a REST API? Pro
- How do retries work in gRPC, and which calls are safe to retry? Pro
- What is gRPC and when would you use it? Pro
- What are microservices and how do REST APIs fit into microservices architecture? Pro
- How do you handle backward compatibility in APIs? Pro
- How do you optimize API response times?
- How do you implement API monitoring and observability? Pro
- How do you design APIs for high availability? Pro
- What is API contract testing and how do you implement it? Pro
- What are the challenges of API deprecation and how do you manage them? Pro
- How do you design APIs for third-party integrations?
- How do you handle data consistency in distributed API systems? Pro
- What strategies do you use for API performance testing? Pro
- How do you implement microservices communication patterns? Pro
- How do you design APIs for scalability? Pro
- How do you design a multi-tenant API so one tenant can never read another tenant's data? Pro
- Walk through the OAuth 2.0 authorization code flow with PKCE, and explain when you would use it. Pro
- How would you design a REST API for a complex domain with relationships? Pro
- What are the security considerations for REST APIs? Pro
- What are webhooks and how do they differ from polling? Pro
- How do you implement API documentation and what are the best practices? Pro
- What is API orchestration vs choreography? Pro
- What are API gateways and service mesh, and how do they differ? Pro
- What are the best practices for API error handling and debugging? Pro
- How do you optimize gRPC performance for high-throughput scenarios? Pro
- How do you implement custom load balancing in gRPC? Pro
- What is gRPC reflection and when would you use it? Pro
- How do you handle gRPC streaming backpressure? Pro
- How do you implement circuit breakers with gRPC? Pro
- How do you implement distributed tracing in gRPC? Pro
- What are the security best practices for gRPC in production? Pro
- How do you handle gRPC service discovery in a microservices architecture? Pro
- How do you implement graceful shutdown for gRPC servers? Pro
- How do you implement request validation in gRPC? Pro
- How do you debug and troubleshoot gRPC issues? Pro
- What is gRPC-Web and when would you use it? Pro
- How do you implement caching strategies with gRPC? Pro
- How do you handle versioning in gRPC services? Pro
- How do you implement comprehensive monitoring for gRPC services? Pro
All questions
Showing of 110What is REST and what are its core principles?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
REST (Representational State Transfer) is an architectural style for distributed systems, defined by Roy Fielding in 2000. It is a set of constraints, not a protocol or a standard.
Six constraints define the style:
- Client-server: the two sides evolve on their own.
- Stateless: each request carries everything the server needs.
- Cacheable: responses must say if they can be stored and reused.
- Uniform interface: one consistent way to address and act on resources.
- Layered system: a client cannot tell if it talks to the origin server.
- Code on demand (optional): the server may send runnable code, like JavaScript.
Every request stands alone, as this one does:
GET /articles/42 HTTP/1.1
Host: api.example.com
Authorization: Bearer <token>
Accept: application/json
Statelessness is the main trade-off. Any server node can handle any request, but each call must resend auth and context.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
Explain the concept of resources in REST API design.
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Resources are the key abstraction in REST. A resource is any information that can be named and addressed. Resources should be:
- Nouns, not verbs: Use
/usersnot/getUsers - Hierarchical:
/users/123/orders/456 - Consistent: Use plural nouns (
/users, not/user) - Meaningful: Clear and descriptive names
Resources represent entities in your domain model and should map to business objects or data entities.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
Explain the difference between PUT and POST methods.
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
POST:
- Creates new resources
- Not idempotent (multiple calls create multiple resources)
- Server determines resource identifier
- Example:
POST /userscreates a new user
PUT:
- Creates or updates resources
- Idempotent (multiple identical calls have same effect)
- Client provides resource identifier
- Example:
PUT /users/123creates or updates user with ID 123
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are the most important HTTP status codes for APIs?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
2xx Success:
- 200 OK: Successful GET, PUT, PATCH
- 201 Created: Successful POST
- 204 No Content: Successful DELETE or PUT with no response body
4xx Client Error:
- 400 Bad Request: Invalid request syntax
- 401 Unauthorized: Authentication required
- 403 Forbidden: Access denied
- 404 Not Found: Resource doesn't exist
- 409 Conflict: Resource conflict
- 422 Unprocessable Entity: Validation errors
5xx Server Error:
- 500 Internal Server Error: Generic server error
- 503 Service Unavailable: Server temporarily unavailable
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What is the difference between authentication and authorization?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Authentication: Verifies who the user is (identity verification)
- "Are you really John Doe?"
- Methods: passwords, biometrics, certificates
Authorization: Determines what the authenticated user can do (permission checking)
- "Can John Doe access this resource?"
- Methods: roles, permissions, ACLs
Both are typically required for secure APIs. Authentication happens first, then authorization checks permissions.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How do you handle validation errors in APIs?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Return 422 Unprocessable Entity with detailed field-level errors:
{
  "error": {
    "code": "VALIDATION_ERROR",
    "message": "Validation failed",
    "details": [
      {
        "field": "email",
        "code": "INVALID_FORMAT",
        "message": "Email must be valid format"
      },
      {
        "field": "password",
        "code": "TOO_SHORT",
        "message": "Password must be at least 8 characters"
      }
    ]
  }
}
This helps clients understand exactly what needs to be fixed.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What is CORS and how do you handle it in APIs?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
CORS (Cross-Origin Resource Sharing) allows controlled access to resources from different domains.
CORS Headers:
Access-Control-Allow-Origin: https://example.com
Access-Control-Allow-Methods: GET, POST, PUT, DELETE
Access-Control-Allow-Headers: Content-Type, Authorization
Access-Control-Max-Age: 3600
Preflight Requests: Browser sends OPTIONS request for complex requests.
Security Considerations:
- Don't use
*for credentials-enabled requests - Be specific with allowed origins
- Validate origins server-side
- Consider using CORS libraries
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are the main HTTP methods used in REST APIs and their purposes?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
The main HTTP methods (verbs) used in REST APIs are:
- GET: Retrieves data from the server. Should be safe and idempotent.
- POST: Creates new resources or submits data for processing.
- PUT: Updates an entire resource or creates it if it doesn't exist. Should be idempotent.
- PATCH: Partially updates a resource.
- DELETE: Removes a resource. Should be idempotent.
- HEAD: Similar to GET but returns only headers, not the body.
- OPTIONS: Returns allowed methods for a resource.
Example:
GET /users/123        # Retrieve user with ID 123
POST /users           # Create a new user
PUT /users/123        # Update entire user 123
PATCH /users/123      # Partially update user 123
DELETE /users/123     # Delete user 123
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are HTTP status codes and give examples of common ones?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
HTTP status codes are three-digit numbers that indicate the result of an HTTP request. They are grouped into five categories:
1xx - Informational:
- 100 Continue
2xx - Success:
- 200 OK: Request successful
- 201 Created: Resource successfully created
- 204 No Content: Successful but no content to return
3xx - Redirection:
- 301 Moved Permanently
- 304 Not Modified
4xx - Client Error:
- 400 Bad Request: Invalid request syntax
- 401 Unauthorized: Authentication required
- 403 Forbidden: Access denied
- 404 Not Found: Resource doesn't exist
- 409 Conflict: Request conflicts with current state
5xx - Server Error:
- 500 Internal Server Error
- 503 Service Unavailable
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What makes an API RESTful?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
An API is considered RESTful when it adheres to REST architectural constraints:
- Uniform Interface: Consistent resource identification (URLs), manipulation through representations, self-descriptive messages, and HATEOAS
- Stateless: Each request is independent and contains all necessary information
- Cacheable: Responses indicate whether they can be cached
- Client-Server: Clear separation of concerns
- Layered System: Can include intermediary layers (proxies, gateways)
- Code on Demand (optional): Server can send executable code to client
Additionally, RESTful APIs typically:
- Use standard HTTP methods appropriately
- Return appropriate HTTP status codes
- Use resource-based URLs (nouns, not verbs)
- Support multiple representations (JSON, XML)
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What is the difference between URI, URL, and URN?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
These are related but distinct concepts:
URI (Uniform Resource Identifier):
- Generic term for any identifier that identifies a resource
- Superset that includes both URLs and URNs
- Example:
mailto:john@example.com
URL (Uniform Resource Locator):
- Type of URI that specifies location and method to access a resource
- Includes protocol, domain, and path
- Example:
https://api.example.com/users/123
URN (Uniform Resource Name):
- Type of URI that identifies a resource by name in a specific namespace
- Location-independent identifier
- Example:
urn:isbn:0451450523
In REST APIs, we primarily work with URLs to locate and access resources over HTTP.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are query parameters and path parameters?
What is JSON and why is it commonly used in REST APIs?
What is Content-Type header and why is it important?
What are Protocol Buffers and why does gRPC use them?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Protocol Buffers (protobuf) are Google's language-neutral, platform-neutral, extensible mechanism for serializing structured data. gRPC uses protobuf for several reasons:
- Efficiency: Binary serialization is faster and more compact than JSON/XML
- Type Safety: Strongly typed schema prevents runtime errors
- Code Generation: Automatically generates client and server code
- Language Agnostic: Works across different programming languages
- Schema Evolution: Supports backward and forward compatibility
Example protobuf definition:
syntax = "proto3";

message User {
  int32 id = 1;
  string name = 2;
  string email = 3;
}

service UserService {
  rpc GetUser(UserRequest) returns (User);
}
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How does gRPC differ from REST APIs?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
| Aspect | gRPC | REST |
|---|---|---|
| Protocol | HTTP/2 | HTTP/1.1 |
| Data Format | Protocol Buffers (binary) | JSON (text) |
| Performance | Faster, lower latency | Slower due to text parsing |
| Streaming | Bidirectional streaming | Limited streaming support |
| Browser Support | Limited (needs gRPC-Web) | Native support |
| Caching | Limited caching capabilities | HTTP caching support |
| Learning Curve | Steeper | Gentler |
| Use Case | Microservices, real-time apps | Web APIs, CRUD operations |
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are the main advantages of using HTTP/2 in gRPC?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
HTTP/2 provides several advantages for gRPC:
- Multiplexing: Multiple requests can be sent simultaneously over a single connection
- Binary Protocol: More efficient parsing compared to HTTP/1.1 text protocol
- Header Compression: Reduces overhead using HPACK compression
- Server Push: Server can send multiple responses for a single request
- Flow Control: Prevents overwhelming slower receivers
- Connection Reuse: Reduces connection overhead and latency
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What types of service methods does gRPC support?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
gRPC supports four types of service methods:
- Unary RPC: Client sends one request, server returns one response
rpc GetUser(UserRequest) returns (User);
- Server Streaming RPC: Client sends one request, server returns a stream of responses
rpc ListUsers(ListUsersRequest) returns (stream User);
- Client Streaming RPC: Client sends a stream of requests, server returns one response
rpc CreateUsers(stream User) returns (CreateUsersResponse);
- Bidirectional Streaming RPC: Both client and server send streams of messages
rpc Chat(stream ChatMessage) returns (stream ChatMessage);
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How do you define a gRPC service in a .proto file?
What is code generation in gRPC and why is it important?
What is a gRPC client stub?
What is the difference between REST and SOAP?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
SOAP is a protocol with a fixed XML message format, while REST is an architectural style. SOAP wraps every call in an XML envelope, and a SOAP service usually publishes a WSDL contract. REST APIs expose resources at URLs and act on them with standard HTTP methods, usually exchanging JSON.
| SOAP | REST | |
|---|---|---|
| Kind | Protocol | Architectural style |
| Format | XML only | Any format, usually JSON |
| Contract | Usually a WSDL | Optional, often OpenAPI |
| Transport | HTTP, SMTP and others | Usually HTTP |
| Caching | Rare, since calls are usually POST |
Standard HTTP caching |
| Security | WS-Security at the message level | TLS plus tokens such as OAuth |
Choose REST for most web and mobile APIs, where lighter payloads and HTTP caching matter. SOAP still fits enterprise systems that need a formal contract or message-level security, such as older banking and insurance integrations.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What is HATEOAS and why is it important?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
HATEOAS (Hypermedia as the Engine of Application State) means that API responses should include links to related actions or resources. This makes APIs self-discoverable and reduces client-server coupling.
Example response with HATEOAS:
{
  "id": 123,
  "name": "John Doe",
  "email": "john@example.com",
  "_links": {
    "self": "/users/123",
    "orders": "/users/123/orders",
    "edit": "/users/123",
    "delete": "/users/123"
  }
}
Benefits include improved API discoverability, reduced documentation needs, and easier API evolution.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
When would you use PATCH vs PUT?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
PUT: Replaces the entire resource with the provided data. If you omit fields, they should be set to default/null values.
PATCH: Partial update of a resource. Only updates the fields provided in the request body.
Example:
PUT /users/123
{
  "name": "John Doe",
  "email": "john@example.com"
}
# Replaces entire user object

PATCH /users/123
{
  "email": "newemail@example.com"
}
# Only updates email field
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
Explain idempotency in API design.
Compare different API authentication methods.
How would you implement role-based access control (RBAC) in an API?
What are the different API versioning strategies?
When should you introduce a new API version?
How should you structure error responses in APIs?
How do you implement pagination in APIs?
What caching strategies can you apply to APIs?
How do you implement rate limiting in APIs?
What are common API security vulnerabilities?
How do you secure API endpoints?
How do you implement API key management?
What is an API Gateway and when would you use one?
Explain the difference between synchronous and asynchronous APIs.
How do you design APIs for mobile applications?
What are webhooks and how do you implement them?
How do you handle file uploads in APIs?
Compare REST vs GraphQL APIs.
How do you handle API documentation and ensure it stays up-to-date?
How do you implement API analytics and usage tracking?
What are API design anti-patterns to avoid?
How do you implement API testing strategies?
How do you design filtering, sorting, and search on a collection endpoint?
How should an API client retry a failed request without making the outage worse?
How would you push real-time updates to API clients? Compare polling, long polling, Server-Sent Events, and WebSockets.
What is idempotency in REST APIs and which HTTP methods are idempotent?
What are the different types of API authentication methods?
What is content negotiation in REST APIs?
How do you handle errors in REST APIs?
What are HTTP response headers commonly used in REST APIs?
What is rate limiting and how is it implemented?
What is pagination and what are different pagination techniques?
What is CORS and how does it affect REST APIs?
What are the considerations for API deprecation?
How do you implement search functionality in REST APIs?
What are the differences between API-first and code-first approaches?
How do you implement real-time features with REST APIs?
What are the security headers important for REST APIs?
How do you handle errors in gRPC?
What is gRPC metadata and how is it used?
What are gRPC interceptors and what are they used for?
How do timeouts and deadlines work in gRPC?
What is connection pooling in gRPC and how does it work?
How do you implement authentication in gRPC?
What are the different load balancing strategies in gRPC?
How do you handle streaming in gRPC?
What is gRPC health checking and how do you implement it?
How do you model a non-CRUD action, like cancelling an order, in a REST API?
How do retries work in gRPC, and which calls are safe to retry?
What is gRPC and when would you use it?
What are microservices and how do REST APIs fit into microservices architecture?
How do you handle backward compatibility in APIs?
How do you optimize API response times?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Database Optimization:
- Use appropriate indexes
- Implement query optimization
- Consider read replicas
- Use connection pooling
Response Optimization:
- Implement field selection:
GET /users?fields=id,name,email - Use compression (gzip)
- Minimize payload size
- Implement lazy loading
Architecture Patterns:
- Async processing for heavy operations
- Background job queues
- Microservices for scalability
- API gateways for routing and caching
Monitoring:
- Track response times
- Monitor error rates
- Implement distributed tracing
- Use APM tools
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How do you implement API monitoring and observability?
How do you design APIs for high availability?
What is API contract testing and how do you implement it?
What are the challenges of API deprecation and how do you manage them?
How do you design APIs for third-party integrations?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Design Considerations:
Developer Experience:
- Clear documentation
- Interactive API explorer
- SDKs in popular languages
- Sandbox environment
Partnership Models:
- Public APIs: Open to all developers
- Partner APIs: Restricted access
- Private APIs: Internal use only
Onboarding Process:
- Self-service registration
- API key management
- Usage tiers and billing
- Support channels
Example Partner API Structure:
POST /partners/webhooks
Authorization: Bearer partner_token
{
  "url": "https://partner.com/webhook",
  "events": ["order.created", "order.updated"],
  "secret": "webhook_secret"
}
Integration Patterns:
- Webhook notifications
- Polling endpoints
- Real-time APIs (WebSockets)
- Batch processing APIs
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How do you handle data consistency in distributed API systems?
What strategies do you use for API performance testing?
How do you implement microservices communication patterns?
How do you design APIs for scalability?
How do you design a multi-tenant API so one tenant can never read another tenant's data?
Walk through the OAuth 2.0 authorization code flow with PKCE, and explain when you would use it.
How would you design a REST API for a complex domain with relationships?
What are the security considerations for REST APIs?
What are webhooks and how do they differ from polling?
How do you implement API documentation and what are the best practices?
What is API orchestration vs choreography?
What are API gateways and service mesh, and how do they differ?
What are the best practices for API error handling and debugging?
How do you optimize gRPC performance for high-throughput scenarios?
How do you implement custom load balancing in gRPC?
What is gRPC reflection and when would you use it?
How do you handle gRPC streaming backpressure?
How do you implement circuit breakers with gRPC?
How do you implement distributed tracing in gRPC?
What are the security best practices for gRPC in production?
How do you handle gRPC service discovery in a microservices architecture?
How do you implement graceful shutdown for gRPC servers?
How do you implement request validation in gRPC?
How do you debug and troubleshoot gRPC issues?
What is gRPC-Web and when would you use it?
How do you implement caching strategies with gRPC?
How do you handle versioning in gRPC services?
How do you implement comprehensive monitoring for gRPC services?
This answer is part of Pro.
The full written answer, with the trade-offs and follow-ups an interviewer will probe.
No matches
Try a different filter or search term.
The core concepts of API Design.
21 concepts in teaching order, one step-by-step diagram each. Go through one, then see every question it answers.
-
1
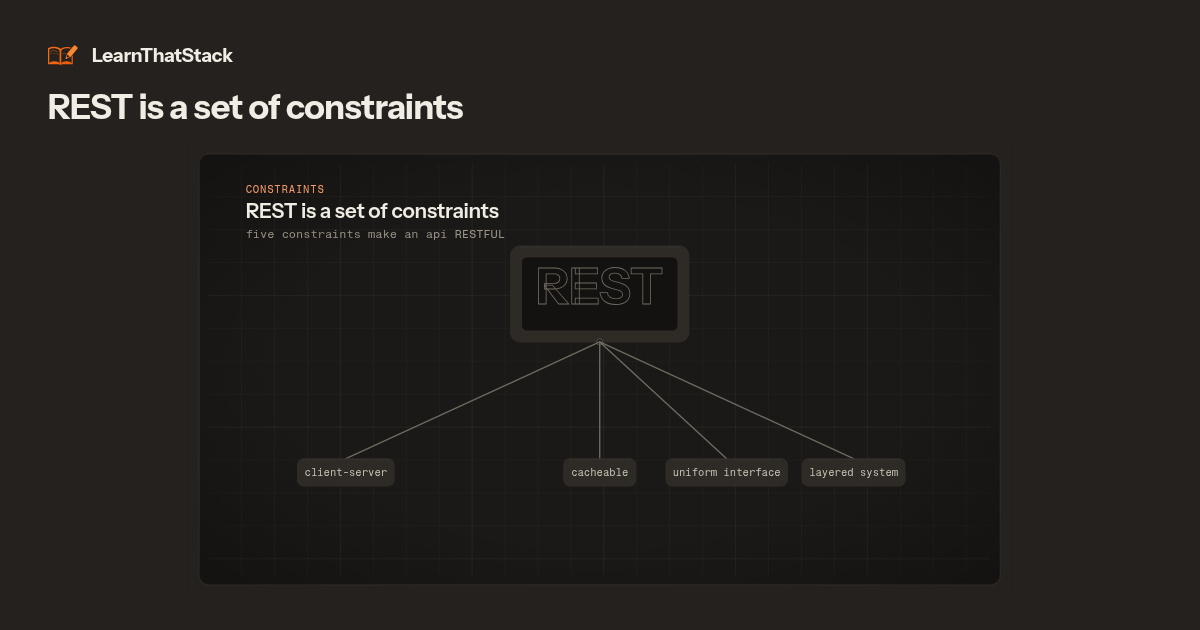 Thinking in resources: what REST actually is
REST is constraints, not JSON over HTTP: address resources, let methods decide the action, send hypermedia links to what's next and more.
Start →
-
2
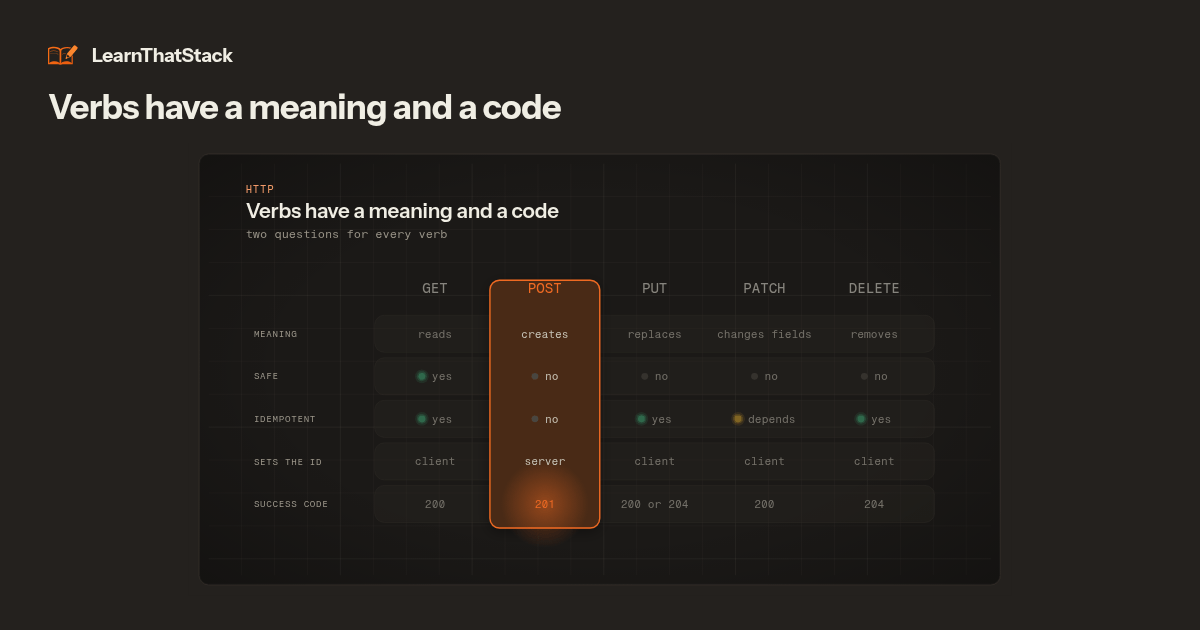 HTTP methods: what each verb promises
A method's promise about safety and idempotency decides when a retry is safe, when a cache is legal, and PUT versus POST.
Start →
-
3
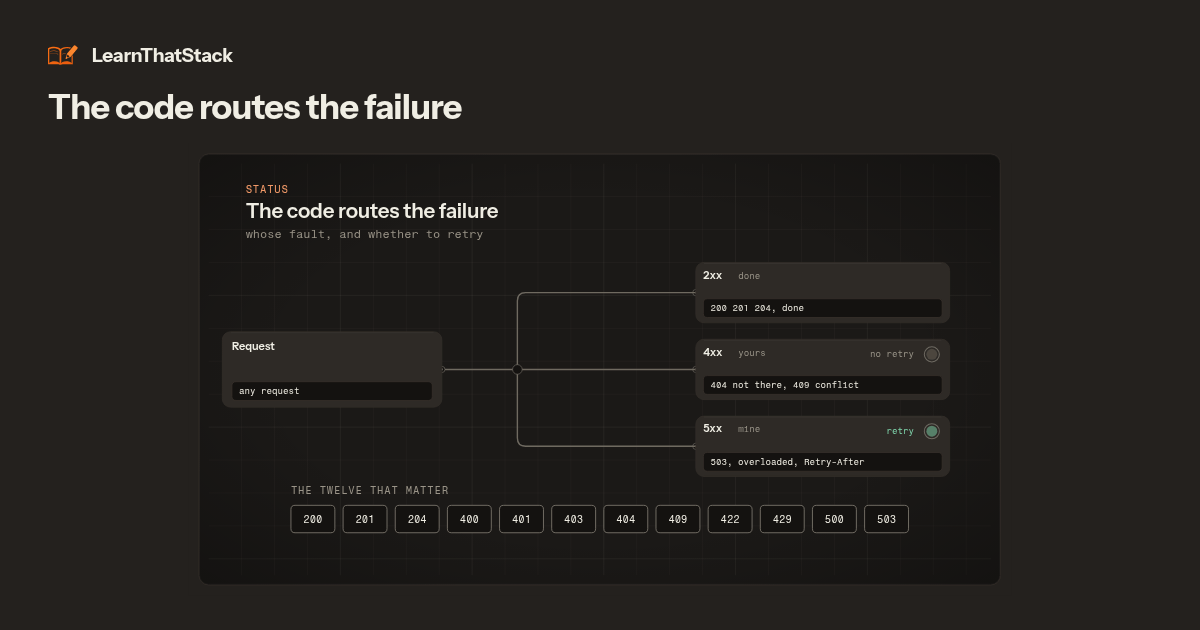 Status codes and error design: how an API says NO
The status code tells machines whose fault the failure was and whether to retry. The error body tells a developer what to fix, and it is never an apology.
Start →
-
4
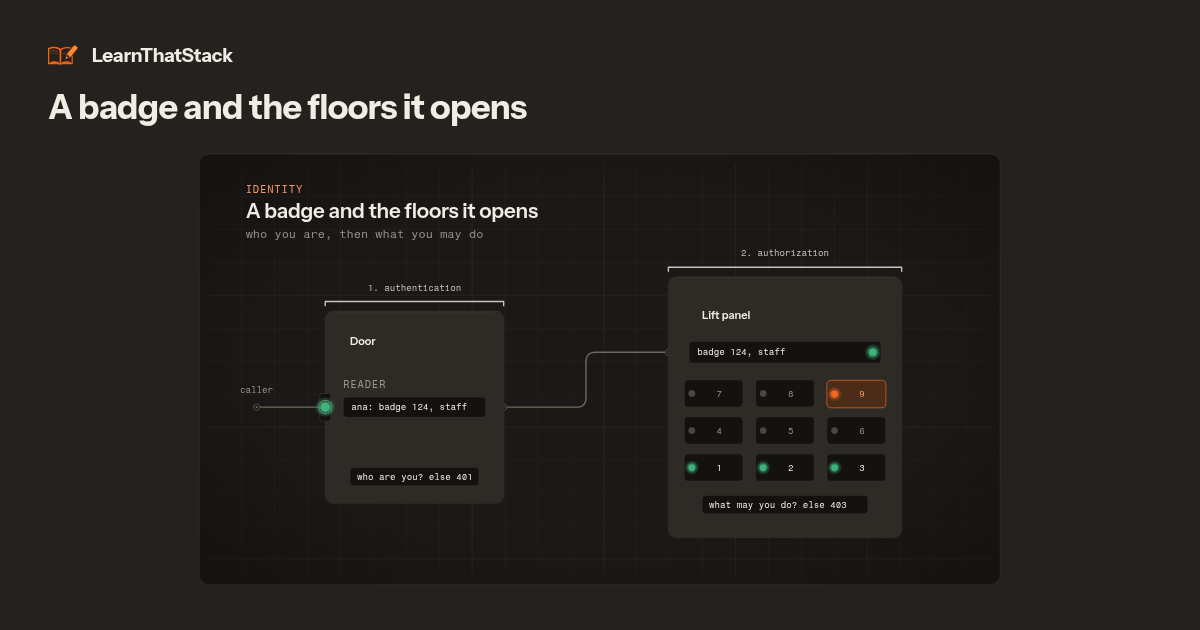 Authentication: proving who is calling
Authentication asks who you are and authorization asks what you may do. Authentication methods differ mainly in where the identity state lives.
Start →
-
5
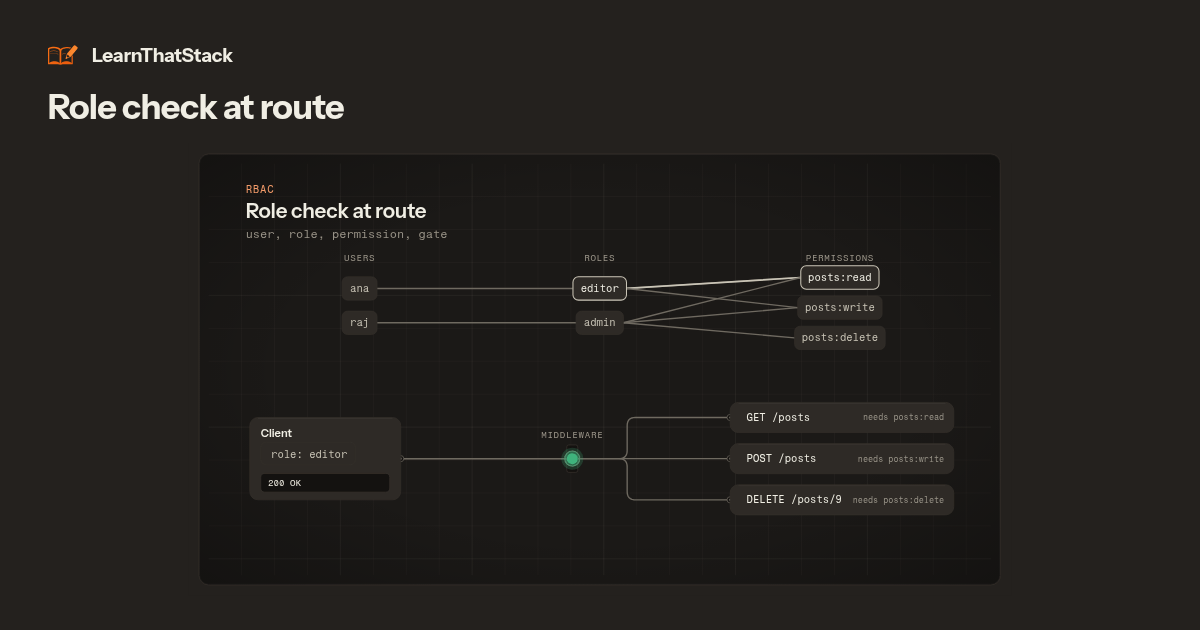 Authorization: a route check is not an object check
A role check at the route is needed but not enough. The most common API breach is never asking whether this user owns object 123.
Unlock →
-
6
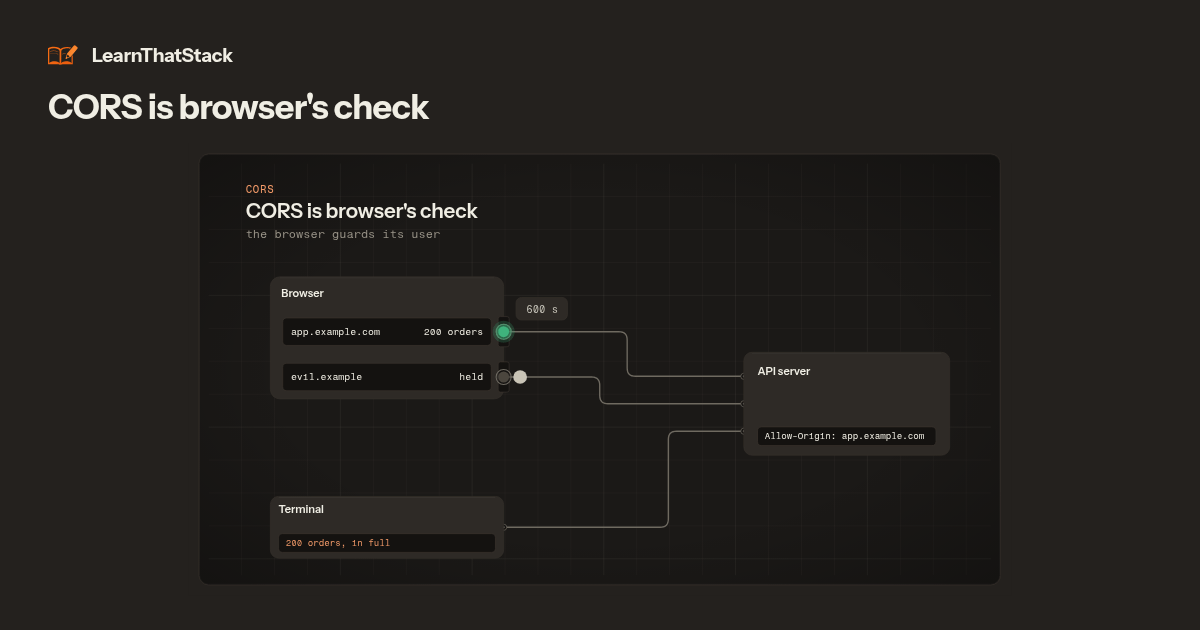 The browser enforces CORS, not your server
The browser runs the same-origin policy to protect its users. And CORS headers tell the browser which origins may read the reply, but requests from curl, POSTMAN don't go through that check.
Start →
-
7
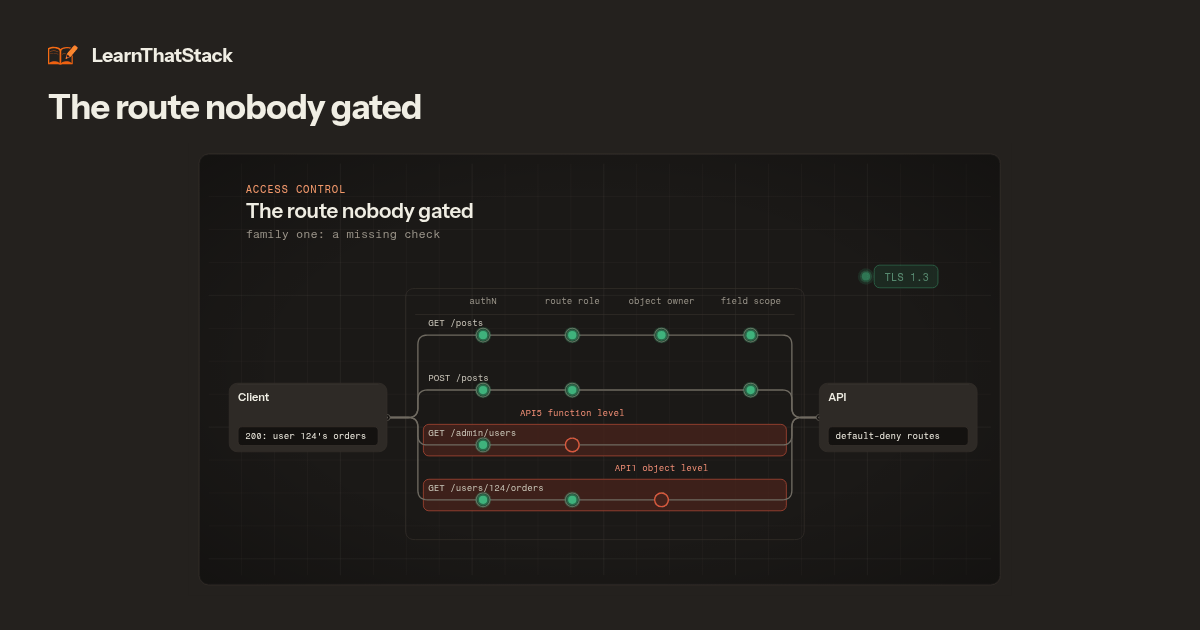 API security: three families of mistakes, not a top ten list
Real breaches come from missing checks, leaked fields and trusted input.
Start →
-
8
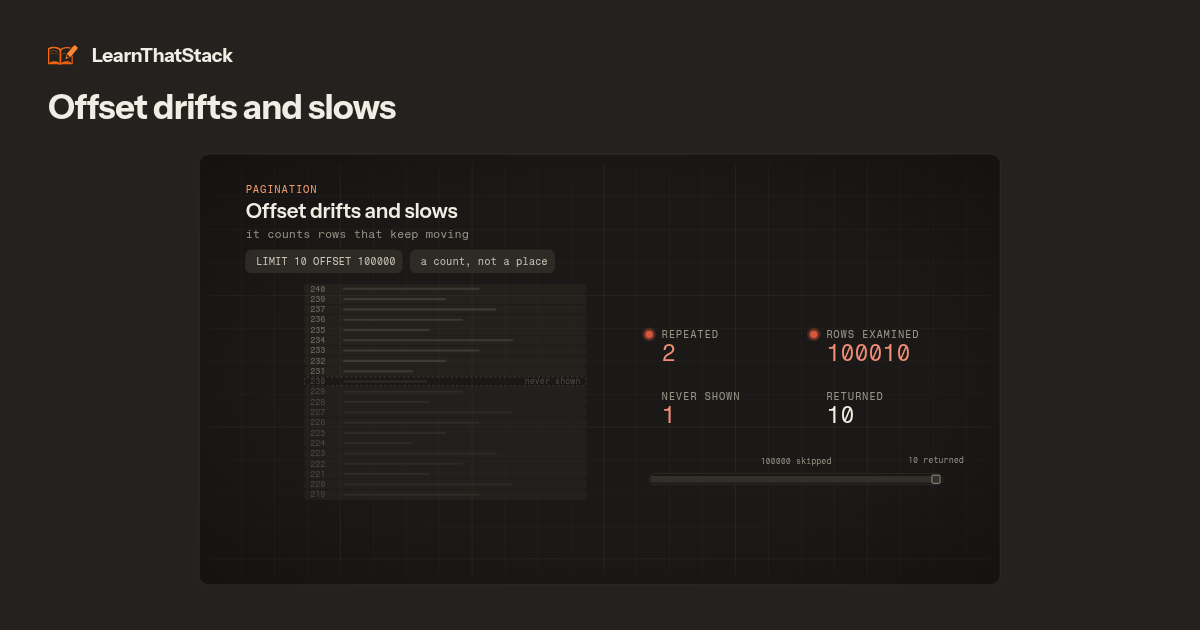 Designing a list endpoint is designing a small query language
Pagination, filtering, sorting and field selection are one problem. Offset paging drifts and slows down. A cursor pins your position to a stable key.
Unlock →
-
9
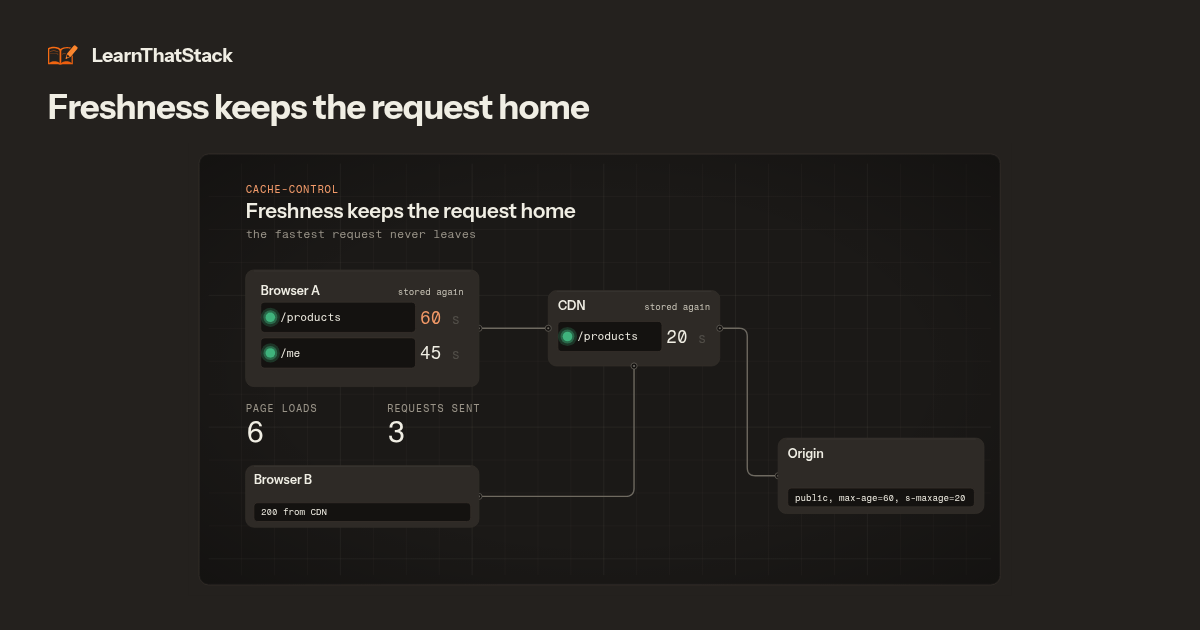 HTTP caching: infrastructure you do not own, working for you
Declare freshness with Cache-Control and identity with ETag, and caches serve your traffic. The hard part is invalidation.
Start →
-
10
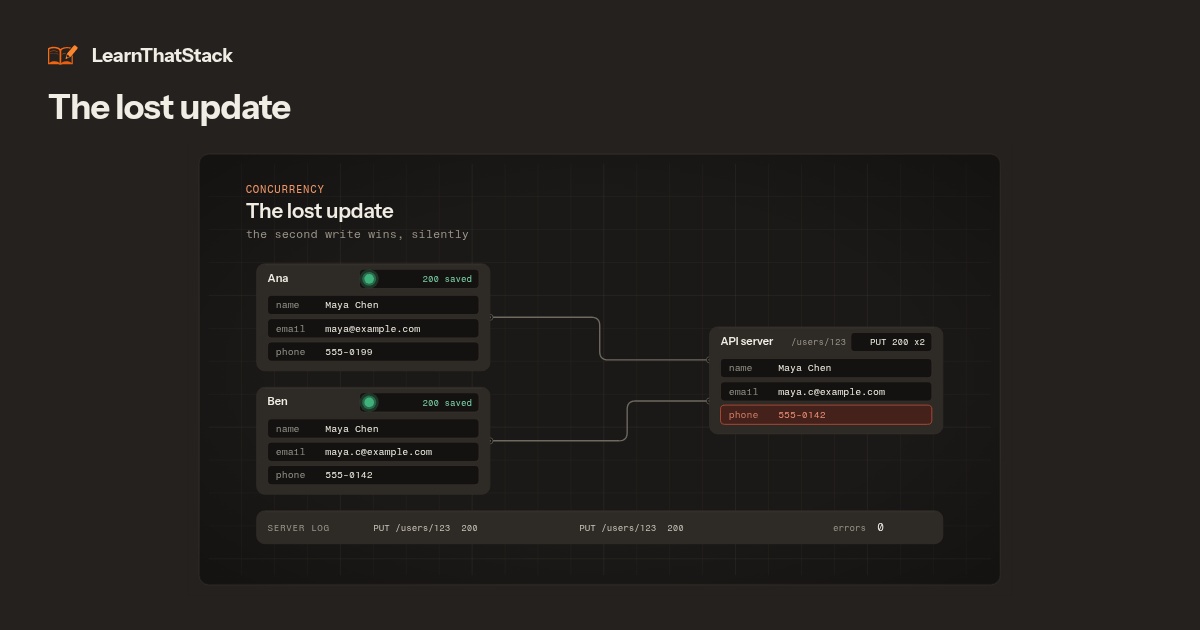 Conditional requests: the lost update and the fix HTTP already has
Two clients read one row and both write it back, and the slower write silently erases the faster one. If-Match makes that loss a loud 412.
Unlock →
-
11
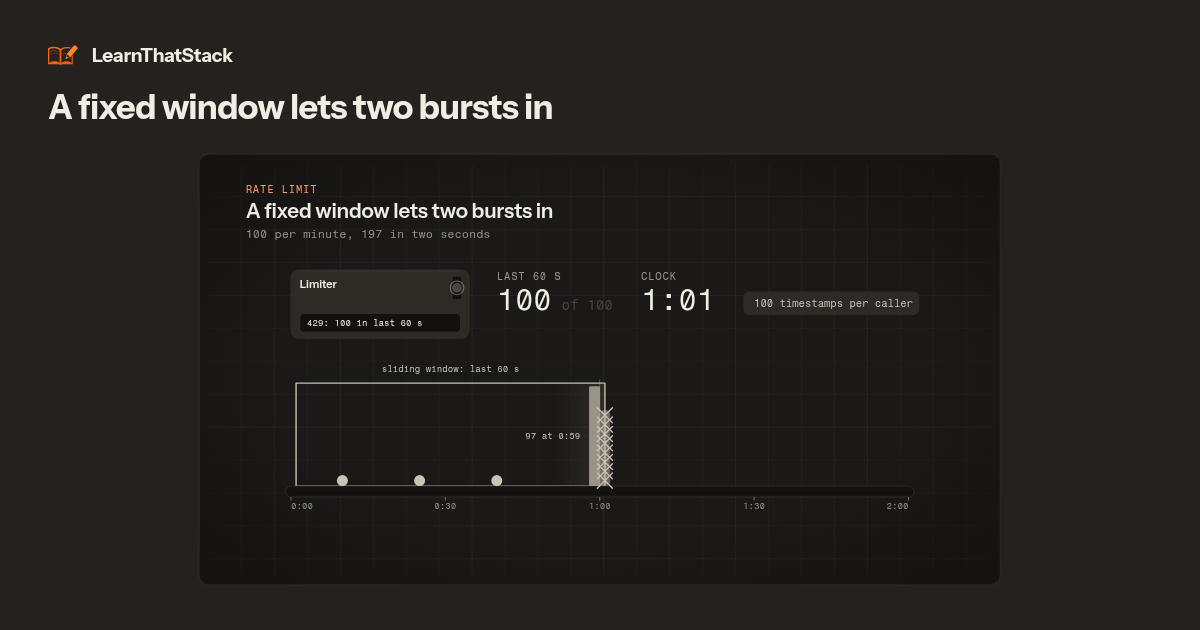 Rate limiting shares capacity fairly, and the algorithm decides how
A limiter protects a shared resource from any one caller, malicious or just retrying badly. The algorithm decides which bursts get through.
Start →
-
12
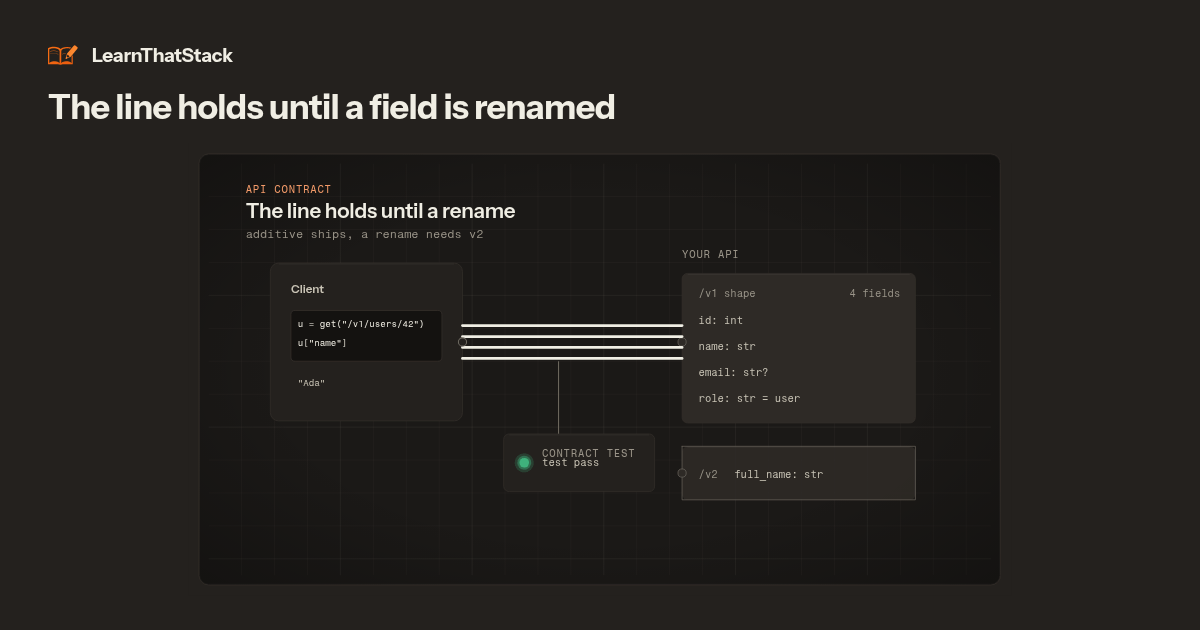 Versioning an API: changing the contract you already published
Only a breaking change needs a new version, and most changes are additive. The deprecation lifecycle matters far more than where the version number goes.
Start →
-
13
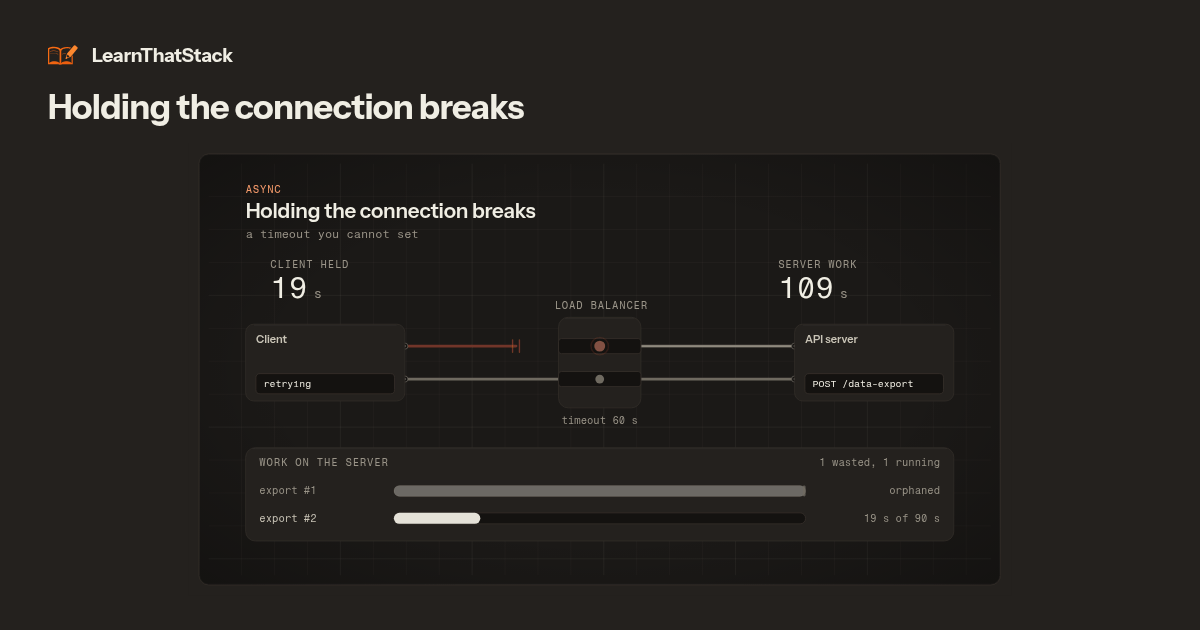 Async APIs and webhooks: when the work takes longer than the request
Do not keep the connection open. Return 202 with a job the client can poll, or send a webhook to whoever needs to know and handle every delivery problem.
Start →
-
14
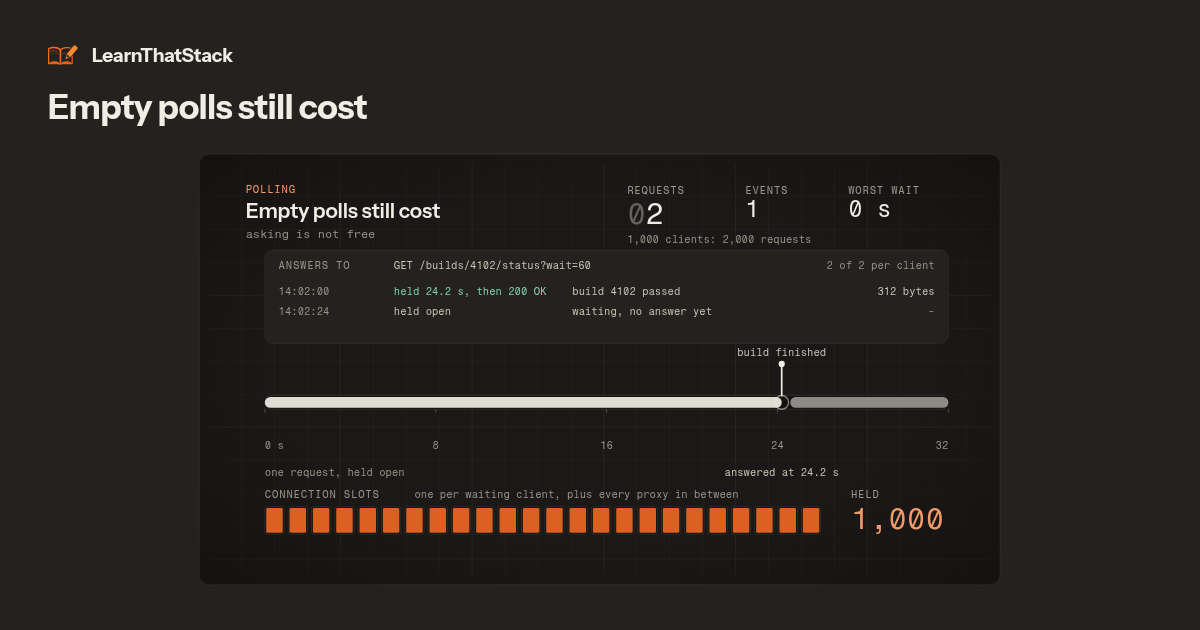 Real-time APIs: step up from polling only for a clear reason
Poll while the delay is acceptable. Push with SSE when only the server has new data, and open a WebSocket only when the client sends messages back.
Unlock →
-
15
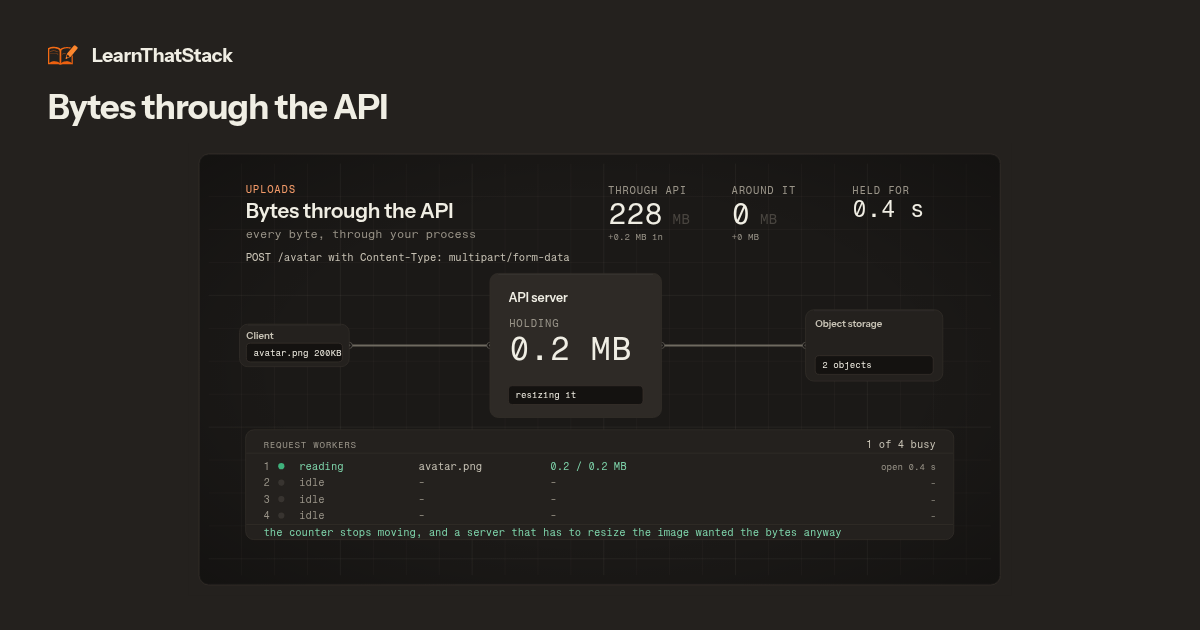 File uploads: do the bytes go through your API or skip it?
Every upload design makes one choice: the bytes go through your API or skip it. A signed URL gives permission to upload, but your API still keeps control.
Unlock →
-
16
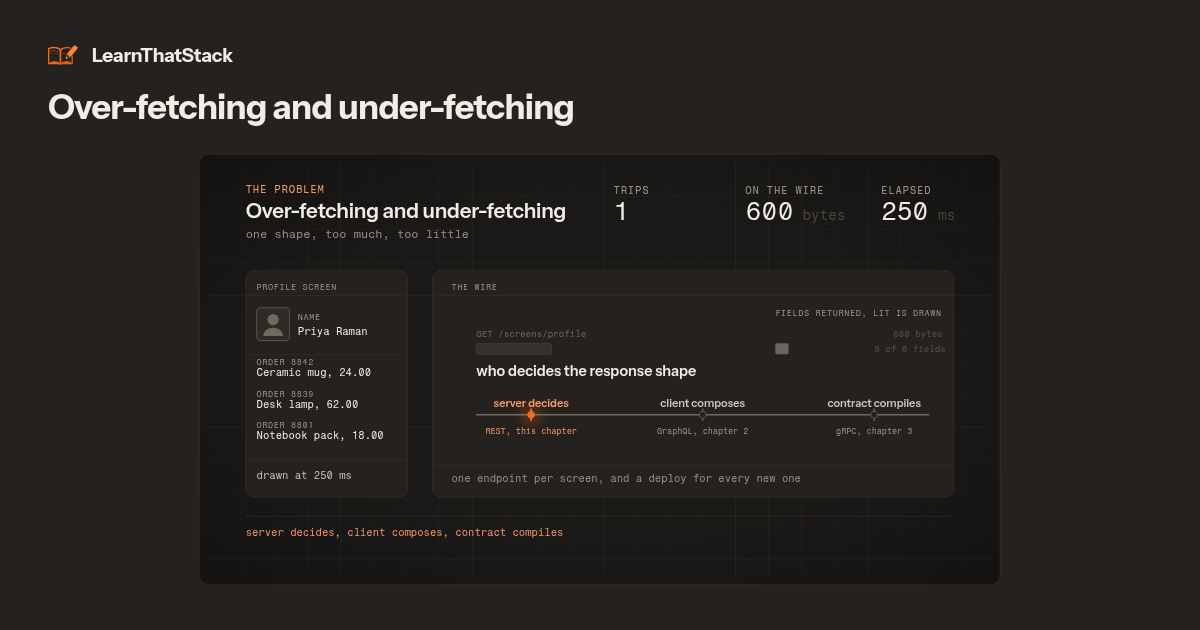 Who controls the response shape
In REST the server decides the response shape, in GraphQL the client builds it, and in gRPC a compiled contract sets it. The trade-offs come from who decides the shape.
Start →
-
17
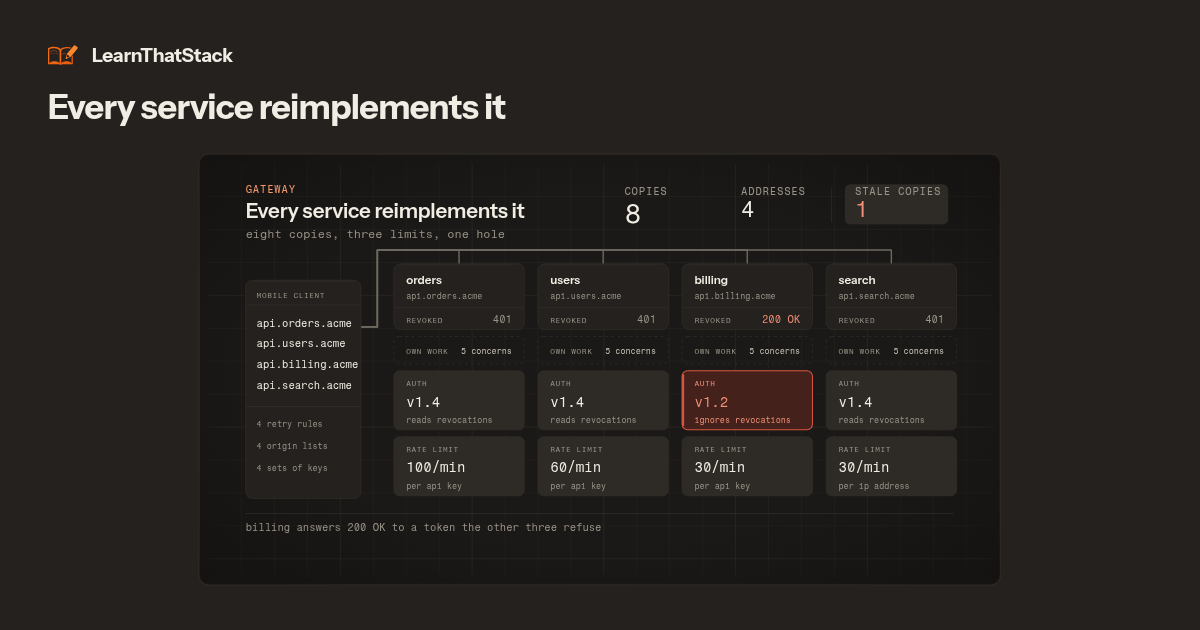 The API gateway: what belongs at the edge
A gateway exists so auth, rate limiting, routing and TLS are implemented once at the edge rather than copied into every service.
Unlock →
-
18
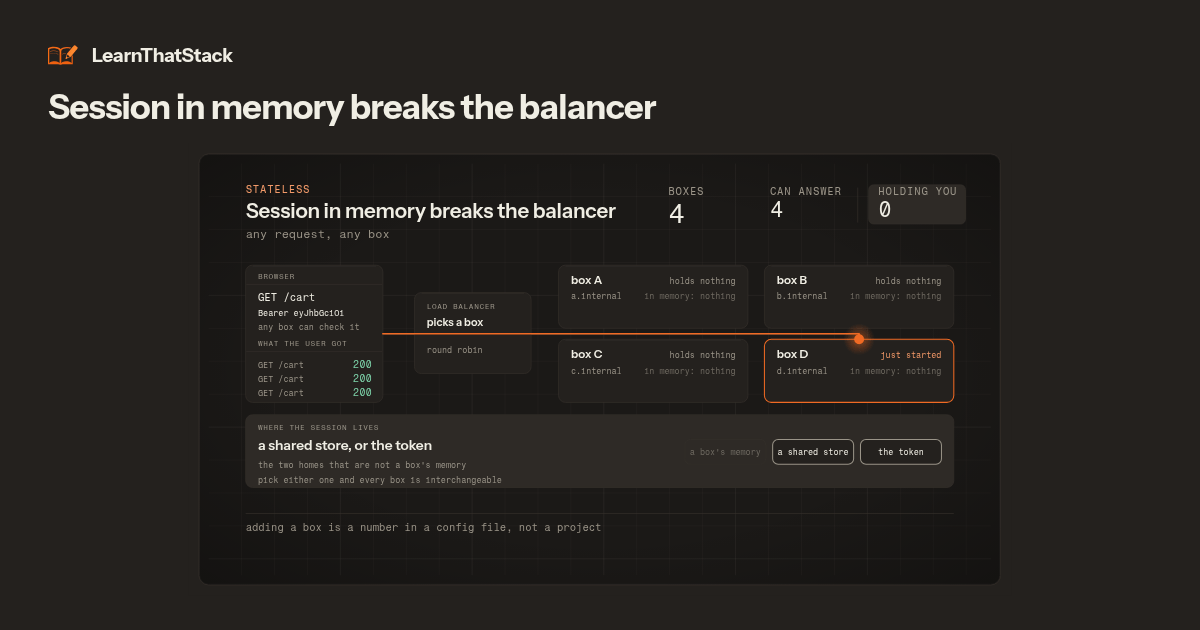 Scale and availability: what statelessness makes possible, and what still fails
Holding no session is what lets the servers scale out. For availability, the other half, assume parts fail and stop one failure from spreading.
Start →
-
19
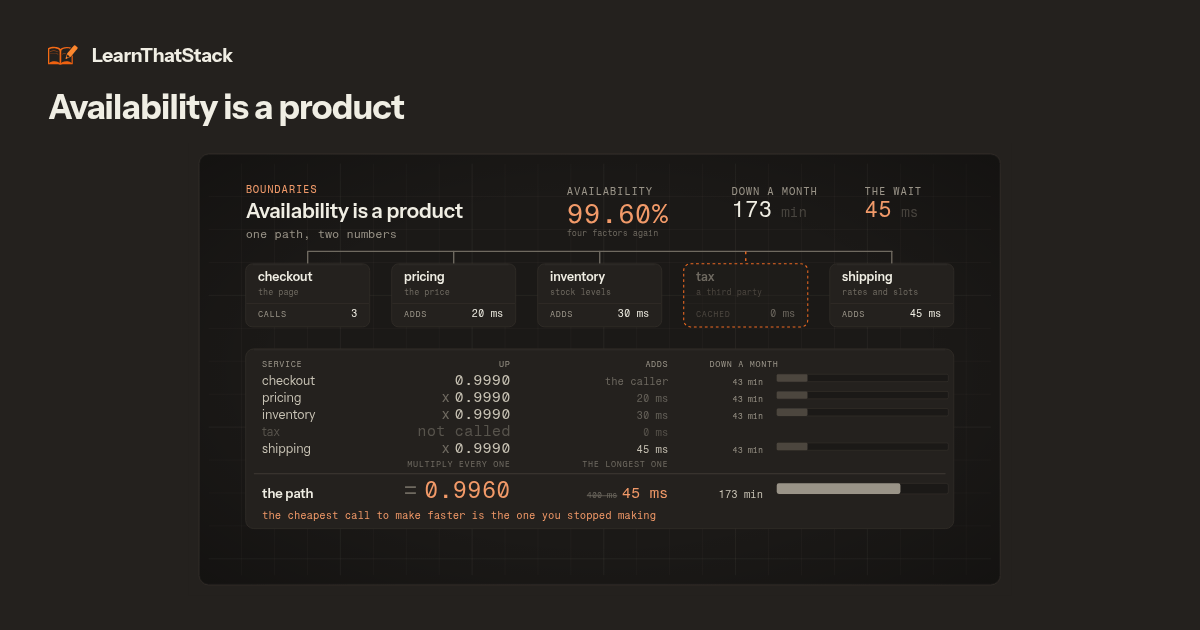 Service boundaries: chains, events, and sagas
Every call you add multiplies the risk. Events decouple services but data agrees later, and a saga replaces a transaction with compensations that undo earlier steps.
Unlock →
-
20
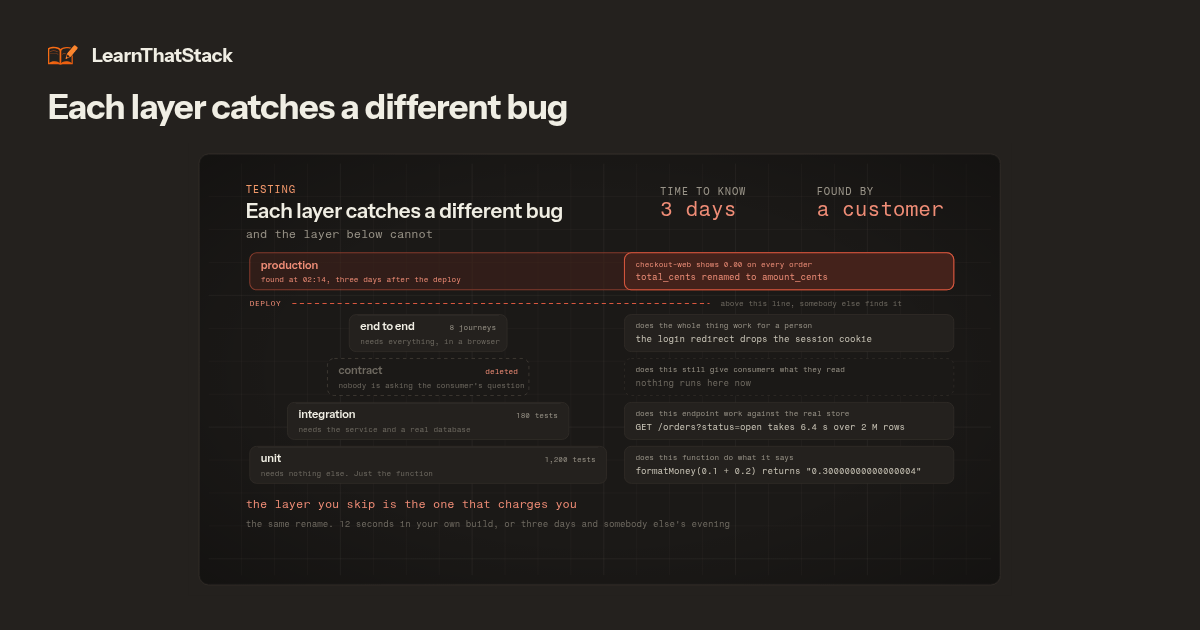 Testing APIs: three different questions
Three suites, three questions: behaviour, compatibility, capacity. The contract test is the one only an API needs.
Start →
-
21
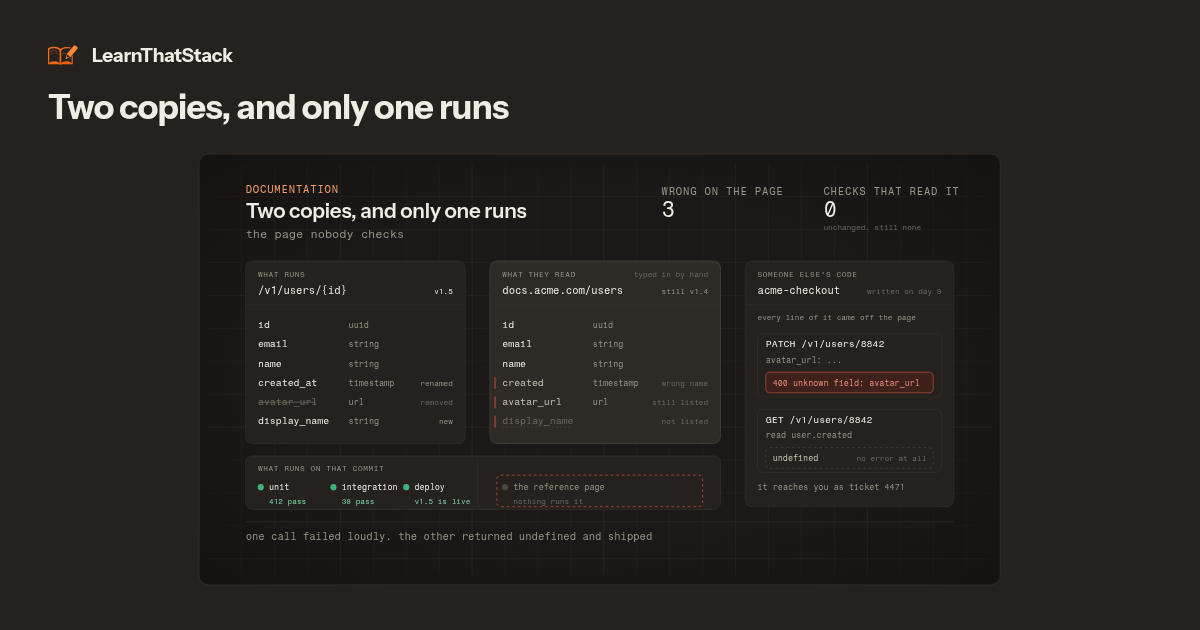 Documentation: the docs come from the spec, not a hand-written copy
Hand-written docs are a second copy of what the code does, and copies go out of date. A spec that generates the reference, clients and checks cannot go out of date.
Start →
API Design, in short videos.
API Design cheatsheet
- Resources & methods01
- Errors & retries02
- Auth & security03
- Paging, caching & speed04
- Versions & change05
- Async & real-time06
- Architecture & scale07
- gRPC basics08
- gRPC in production09
- Docs, tests & monitoring10
- The model11
- + 5 more inside
90 of 110 API Design answers are in Pro.
Full answers, code samples, and AI explanations that go simpler or deeper. Cancel anytime.
- Full answers + code
- AI explanations, simpler or deeper
- 1,000 AI credits / month
- Cancel anytime
Change topic
Pick a different technology or stack. Your current topic stays put until you choose a new one.
MEAN
MongoDB, Express, Angular, Node.jsMERN
MongoDB, Express, React, Node.jsDjango
Python Full-Stack DevelopmentRuby on Rails
Convention over ConfigurationServerless on AWS
Serverless Architecture on AWSInterviewers also test these - they're common to every stack, whichever one you picked above.
Flutter Mobile
Flutter Cross-Platform Mobile DevelopmentInterviewers also test these - they're common to every stack, whichever one you picked above.
Spring Boot
Enterprise Java Development.NET
Microsoft EcosystemVue
Vue.js, Vite, TypeScript, Tailwind, Node.jsGo Backend
Golang, gRPC, PostgreSQL, Redis, RabbitMQInterviewers also test these - they're common to every stack, whichever one you picked above.
FastAPI
Python, FastAPI, SQLAlchemy, PostgreSQLReact Native
React, TypeScript, Redux, FirebaseiOS Native
Swift, SwiftUI, UIKit, FirebaseAndroid Native
Java, Jetpack Compose, FirebaseDevOps / Platform
Docker, Kubernetes, Terraform, CI/CDInterviewers also test these - they're common to every stack, whichever one you picked above.
AI Engineer
LLMs, RAG, Agents, EvalsAI-Powered Developer
Claude Code, Copilot, Agentic WorkflowsCore SWE Interview Prep
Data structures, algorithms, OS, concurrency, networking, gitInterviewers also test these - they're common to every stack, whichever one you picked above.
Interviewers also test these - they're common to every stack, whichever one you picked above.