Practise API Design one question at a time. Answer out loud or in writing, get graded, and see exactly what you missed.
What is REST and what are its core principles?
REST (Representational State Transfer) is an architectural style for distributed systems, defined by Roy Fielding in 2000. It is a set of constraints, not a protocol or a standard.
Six constraints define the style:
- Client-server: the two sides evolve on their own.
- Stateless: each request carries everything the server needs.
- Cacheable: responses must say if they can be stored and reused.
- Uniform interface: one consistent way to address and act on resources.
- Layered system: a client cannot tell if it talks to the origin server.
- Code on demand (optional): the server may send runnable code, like JavaScript.
Every request stands alone, as this one does:
GET /articles/42 HTTP/1.1
Host: api.example.com
Authorization: Bearer <token>
Accept: application/json
Statelessness is the main trade-off. Any server node can handle any request, but each call must resend auth and context.
Missed:
“PUT updates the whole resource and PATCH updates only some fields. If I'm only changing the email I'd use PATCH, and PUT when I'm sending the full object.”
Partly thereYou have the basic split: PUT for the full object, PATCH for a partial change. That is only the definition. The question asks when to use each, and you left out idempotency and stale-overwrite risk, which drive the choice.
Missed: No mention of idempotency. PUT is safe to retry, while PATCH such as 'append an item' is not guaranteed to be.
Missed: Does not say that fields omitted from a PUT body get reset to default or null.
Missed: No mention of the stale-copy overwrite risk with PUT or of using ETag and If-Match to guard against it.
Get your own answers graded
Sign up free. Your account comes with 50 credits for grading, and it remembers what you missed.
What it covers
- REST and resource design
- HTTP methods, status codes and errors
- Collections and payload design
- Authentication and authorization
- API security and rate limiting
- Versioning and compatibility
- API styles and real-time delivery
- gRPC fundamentals
- Performance, reliability and observability
- Testing, documentation and developer experience
- Scale and distributed systems
- gRPC in production
All 92 questions
REST and resource design
REST constraints, modeling resources as nouns in URLs, hypermedia links and the common URL and design anti-patterns to avoid.
- What is REST and what are its core principles?
- Explain the concept of resources in REST API design.
- What is the difference between URI, URL, and URN?
- What are query parameters and path parameters? Pro
- What is HATEOAS and why is it important?
- What are API design anti-patterns to avoid? Pro
- How do you model a non-CRUD action, like cancelling an order, in a REST API? Pro
- How would you design a REST API for a complex domain with relationships? Pro
HTTP methods, status codes and errors
Choosing between POST, PUT and PATCH and which calls are safe to repeat, picking status codes and headers, and returning consistent error bodies.
- Explain the difference between PUT and POST methods.
- What are the most important HTTP status codes for APIs?
- How do you handle validation errors in APIs?
- What are the main HTTP methods used in REST APIs and their purposes?
- When would you use PATCH vs PUT?
- Explain idempotency in API design. Pro
- How should you structure error responses in APIs? Pro
- What are HTTP response headers commonly used in REST APIs? Pro
Collections and payload design
Paginating, filtering and sorting collections, handling file uploads and keeping payloads lean for mobile clients.
- What is JSON and why is it commonly used in REST APIs? Pro
- What is the Content-Type header and why is it important? Pro
- How do you implement pagination in APIs? Pro
- How do you design APIs for mobile applications? Pro
- How do you handle file uploads in APIs? Pro
- How do you design filtering, sorting, and search on a collection endpoint? Pro
- What is content negotiation in REST APIs? Pro
Authentication and authorization
Verifying who is calling and what they may do: API keys, JWT, OAuth with PKCE and role-based access control.
- What is the difference between authentication and authorization?
- Compare different API authentication methods. Pro
- How would you implement role-based access control (RBAC) in an API? Pro
- How do you implement API key management? Pro
- Walk through the OAuth 2.0 authorization code flow with PKCE, and explain when you would use it. Pro
API security and rate limiting
Defending endpoints against common vulnerabilities, cross-origin access, abuse through rate limits and leaks between tenants.
- What is CORS and how do you handle it in APIs?
- How do you implement rate limiting in APIs? Pro
- What are common API security vulnerabilities? Pro
- How do you secure API endpoints? Pro
- What are the security headers important for REST APIs? Pro
- How do you design a multi-tenant API so one tenant can never read another tenant's data? Pro
Versioning and compatibility
Versioning strategies, telling breaking from safe changes, keeping old clients working and retiring endpoints.
API styles and real-time delivery
REST vs GraphQL vs gRPC, sync vs async operations, webhooks and pushing live updates to clients.
- How does gRPC differ from REST APIs?
- What is the difference between REST and SOAP?
- Explain the difference between synchronous and asynchronous APIs. Pro
- What are webhooks and how do you implement them? Pro
- Compare REST vs GraphQL APIs. Pro
- How would you push real-time updates to API clients? Compare polling, long polling, Server-Sent Events, and WebSockets. Pro
- What is gRPC and when would you use it? Pro
gRPC fundamentals
Protocol Buffers and .proto contracts, HTTP/2, the four method types and streaming, generated stubs, metadata, deadlines, status codes and interceptors.
- What are Protocol Buffers and why does gRPC use them?
- What are the main advantages of using HTTP/2 in gRPC?
- What types of service methods does gRPC support?
- How do you define a gRPC service in a .proto file? Pro
- What is code generation in gRPC and why is it important? Pro
- How do you handle errors in gRPC? Pro
- What is gRPC metadata and how is it used? Pro
- What are gRPC interceptors and what are they used for? Pro
- How do timeouts and deadlines work in gRPC? Pro
- How do you handle streaming in gRPC? Pro
- What is gRPC reflection and when would you use it? Pro
- How do you implement request validation in gRPC? Pro
- What is gRPC-Web and when would you use it? Pro
- How do you handle versioning in gRPC services? Pro
Performance, reliability and observability
Caching and faster responses, load testing, staying available through failures, retrying safely, and monitoring and tracking how the API is used.
- What caching strategies can you apply to APIs? Pro
- How do you implement API analytics and usage tracking? Pro
- How should an API client retry a failed request without making the outage worse? Pro
- How do you optimize API response times?
- How do you implement API monitoring and observability? Pro
- How do you design APIs for high availability? Pro
- What strategies do you use for API performance testing? Pro
Testing, documentation and developer experience
Testing APIs and their contracts, keeping docs accurate and making the API easy for third parties to adopt.
- How do you handle API documentation and ensure it stays up-to-date? Pro
- How do you implement API testing strategies? Pro
- What are the differences between API-first and code-first approaches? Pro
- What is API contract testing and how do you implement it? Pro
- How do you design APIs for third-party integrations?
Scale and distributed systems
Scaling APIs horizontally, API gateways and service meshes, microservices communication and coordination, and keeping data consistent across services.
- What is an API Gateway and when would you use one? Pro
- What are microservices and how do REST APIs fit into microservices architecture? Pro
- How do you handle data consistency in distributed API systems? Pro
- How do you implement microservices communication patterns? Pro
- How do you design APIs for scalability? Pro
- What is the difference between API orchestration and choreography? Pro
- What are API gateways and service mesh, and how do they differ? Pro
gRPC in production
Running gRPC services: connections and load balancing, service discovery and health checks, security, resilience, performance, caching and observability.
- What is connection pooling in gRPC and how does it work? Pro
- How do you implement authentication in gRPC? Pro
- What are the different load balancing strategies in gRPC? Pro
- What is gRPC health checking and how do you implement it? Pro
- How do retries work in gRPC, and which calls are safe to retry? Pro
- How do you optimize gRPC performance for high-throughput scenarios? Pro
- How do you handle gRPC streaming backpressure? Pro
- How do you implement circuit breakers with gRPC? Pro
- How do you implement distributed tracing in gRPC? Pro
- What are the security best practices for gRPC in production? Pro
- How do you handle gRPC service discovery in a microservices architecture? Pro
- How do you implement graceful shutdown for gRPC servers? Pro
- How do you debug and troubleshoot gRPC issues? Pro
- How do you implement caching strategies with gRPC? Pro
All questions
Showing of 92What is REST and what are its core principles?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
REST (Representational State Transfer) is an architectural style for distributed systems, defined by Roy Fielding in 2000. It is a set of constraints, not a protocol or a standard.
Six constraints define the style:
- Client-server: the two sides evolve on their own.
- Stateless: each request carries everything the server needs.
- Cacheable: responses must say if they can be stored and reused.
- Uniform interface: one consistent way to address and act on resources.
- Layered system: a client cannot tell if it talks to the origin server.
- Code on demand (optional): the server may send runnable code, like JavaScript.
Every request stands alone, as this one does:
GET /articles/42 HTTP/1.1
Host: api.example.com
Authorization: Bearer <token>
Accept: application/json
Statelessness is the main trade-off. Any server node can handle any request, but each call must resend auth and context.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
Explain the concept of resources in REST API design.
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Resources are the key abstraction in REST. A resource is any information that can be named and addressed. Resources should be:
- Nouns, not verbs: Use
/usersnot/getUsers - Hierarchical:
/users/123/orders/456 - Consistent: Use plural nouns (
/users, not/user) - Meaningful: Clear and descriptive names
Resources represent entities in your domain model and should map to business objects or data entities.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
Explain the difference between PUT and POST methods.
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
POST asks the server to create a new resource and choose its identifier. PUT creates or updates the resource at an identifier the client provides. So POST /users creates a new user, while PUT /users/123 creates or updates the user with ID 123.
The other difference is what a repeat does. POST is not idempotent, because multiple calls create multiple resources. PUT is idempotent, because multiple identical calls have the same effect as one.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are the most important HTTP status codes for APIs?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
The core codes are 200 OK, 400 Bad Request and 500 Internal Server Error. The first digit gives the class: 2xx means success, 4xx a client error and 5xx a server error.
200 OKfor a successfulGET,PUTorPATCH.201 Createdfor a successfulPOST.204 No Contentfor a successfulDELETEorPUTwith no response body.400 Bad Requestfor invalid request syntax.401 Unauthorizedwhen authentication is required.403 Forbiddenwhen access is denied.404 Not Foundfor a missing resource.409 Conflictwhen the request conflicts with the current state.422 Unprocessable Contentwhen the body parses but fails validation.500 Internal Server Errorfor a generic server error.503 Service Unavailablewhen the server is temporarily unavailable.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What is the difference between authentication and authorization?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Authentication checks who you are, and authorization checks what you may do. Authentication happens first, then authorization checks the permissions of the identity it proved.
| Authentication | Authorization | |
|---|---|---|
| Question | "Are you really John Doe?" | "Can John Doe access this resource?" |
| Verifies | Identity | Permissions |
| Methods | Passwords, biometrics, certificates | Roles, permissions, ACLs |
| Failure status | 401 Unauthorized |
403 Forbidden |
The status codes follow the same split. Return 401 when credentials are missing or invalid, since the client needs to authenticate. Despite its name, 401 Unauthorized means unauthenticated. Return 403 when the server knows the caller but refuses the request. Secure APIs need both checks.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How do you handle validation errors in APIs?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Reject the request with 422 Unprocessable Content and list every failing field, so the client can fix them all in one round trip. Use 400 Bad Request instead when the body can't be parsed at all, such as malformed JSON.
{
  "error": {
    "code": "VALIDATION_ERROR",
    "message": "Validation failed",
    "details": [
      {
        "field": "email",
        "code": "INVALID_FORMAT",
        "message": "Email must be valid format"
      },
      {
        "field": "password",
        "code": "TOO_SHORT",
        "message": "Password must be at least 8 characters"
      }
    ]
  }
}
Each entry carries three things.
- A
fieldthat names the input, so a form can highlight it. - A stable error code, such as
TOO_SHORT, that clients can handle in code. - A human message for display.
Validate the whole body before acting, and return all the errors at once rather than stopping at the first. Keep the shape consistent with your other errors, or use the standard problem details format from RFC 9457 with an errors member.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What is CORS and how do you handle it in APIs?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Cross-Origin Resource Sharing (CORS) lets a server tell browsers which other origins may call it. By default a browser stops a page's script from reading another origin's responses, and CORS headers relax that rule in a controlled way.
An origin is the scheme, host and port together, so https://app.example.com and https://api.example.com are different origins. The server declares what it allows.
Access-Control-Allow-Origin: https://example.com
Access-Control-Allow-Methods: GET, POST, PUT, DELETE
Access-Control-Allow-Headers: Content-Type, Authorization
Access-Control-Max-Age: 3600
For a request that isn't simple, such as a PUT or one with an Authorization header, the browser first sends a preflight OPTIONS request. Access-Control-Max-Age lets the browser cache that answer.
Handle it with a CORS library rather than by hand.
- Be specific with allowed origins, and don't use
*for requests with credentials. - Validate the
Originheader against an allowlist on the server. - CORS only guides browsers. Other clients ignore it, so it never replaces authentication.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are the main HTTP methods used in REST APIs and their purposes?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
REST APIs map each action on a resource to one of the HTTP methods.
GETretrieves data from the server. It should be safe and idempotent.POSTcreates new resources or submits data for processing.PUTupdates an entire resource, or creates it if it doesn't exist. It should be idempotent.PATCHpartially updates a resource.DELETEremoves a resource. It should be idempotent.HEADworks likeGETbut returns only headers, not the body.OPTIONSreturns the methods allowed for a resource.
Here they are applied to one user resource.
GET /users/123        # Retrieve user with ID 123
POST /users           # Create a new user
PUT /users/123        # Update entire user 123
PATCH /users/123      # Partially update user 123
DELETE /users/123     # Delete user 123
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What is the difference between URI, URL, and URN?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
These are related but distinct concepts:
URI (Uniform Resource Identifier):
- Generic term for any identifier that identifies a resource
- Superset that includes both URLs and URNs
- Example:
mailto:john@example.com
URL (Uniform Resource Locator):
- Type of URI that specifies location and method to access a resource
- Includes protocol, domain, and path
- Example:
https://api.example.com/users/123
URN (Uniform Resource Name):
- Type of URI that identifies a resource by name in a specific namespace
- Location-independent identifier
- Example:
urn:isbn:0451450523
In REST APIs, we primarily work with URLs to locate and access resources over HTTP.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are query parameters and path parameters?
What is JSON and why is it commonly used in REST APIs?
What is the Content-Type header and why is it important?
What are Protocol Buffers and why does gRPC use them?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Protocol Buffers (protobuf) are Google's language-neutral, platform-neutral, extensible mechanism for serializing structured data. gRPC uses protobuf for several reasons:
- Efficiency: Binary serialization is faster and more compact than JSON/XML
- Type Safety: Strongly typed schema prevents runtime errors
- Code Generation: Automatically generates client and server code
- Language Agnostic: Works across different programming languages
- Schema Evolution: Supports backward and forward compatibility
Example protobuf definition:
syntax = "proto3";

message User {
  int32 id = 1;
  string name = 2;
  string email = 3;
}

service UserService {
  rpc GetUser(UserRequest) returns (User);
}
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How does gRPC differ from REST APIs?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
gRPC and REST differ mainly in the contract and the wire format. gRPC uses a strict Protocol Buffers contract, sends binary messages over HTTP/2 and streams in both directions. REST uses resources and HTTP verbs with JSON, which any browser or tool can read.
| Aspect | gRPC | REST |
|---|---|---|
| Protocol | HTTP/2 | HTTP/1.1 or HTTP/2 |
| Data Format | Binary Protocol Buffers | Text JSON |
| Performance | Faster, lower latency | Slower due to text parsing |
| Streaming | Bidirectional streaming | Limited streaming support |
| Browser Support | Needs gRPC-Web | Native support |
| Caching | Limited caching capabilities | HTTP caching support |
| Learning Curve | Steeper | Gentler |
| Use Case | Microservices, real-time apps | Web APIs, CRUD operations |
Choose gRPC for internal service-to-service calls where speed and typed clients matter. Choose REST for public and browser-facing APIs, where HTTP caching and plain JSON help more than raw speed.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What are the main advantages of using HTTP/2 in gRPC?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
HTTP/2 lets gRPC run many calls at once over one connection, in a compact binary format.
- Multiplexing sends many requests and responses at the same time over a single connection.
- Binary framing is cheaper to parse than the text protocol of HTTP/1.1.
- Header compression with HPACK cuts the bytes spent on repeated headers.
- Flow control stops a fast sender from overwhelming a slow receiver.
- Reusing one connection avoids new handshakes and cuts latency.
HTTP/2 also defines server push, but gRPC doesn't use it. The grpc-java client turns push off in its HTTP/2 settings, for example. Server streaming covers the case of many responses to one request.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What types of service methods does gRPC support?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
gRPC supports four types of service methods:
- Unary RPC: Client sends one request, server returns one response
rpc GetUser(UserRequest) returns (User);
- Server Streaming RPC: Client sends one request, server returns a stream of responses
rpc ListUsers(ListUsersRequest) returns (stream User);
- Client Streaming RPC: Client sends a stream of requests, server returns one response
rpc CreateUsers(stream User) returns (CreateUsersResponse);
- Bidirectional Streaming RPC: Both client and server send streams of messages
rpc Chat(stream ChatMessage) returns (stream ChatMessage);
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How do you define a gRPC service in a .proto file?
What is code generation in gRPC and why is it important?
What is the difference between REST and SOAP?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
SOAP is a protocol with a fixed XML message format, while REST is an architectural style. SOAP wraps every call in an XML envelope, and a SOAP service usually publishes a WSDL contract. REST APIs expose resources at URLs and act on them with standard HTTP methods, usually exchanging JSON.
| SOAP | REST | |
|---|---|---|
| Kind | Protocol | Architectural style |
| Format | XML only | Any format, usually JSON |
| Contract | Usually a WSDL | Optional, often OpenAPI |
| Transport | HTTP, SMTP and others | Usually HTTP |
| Caching | Rare, since calls are usually POST |
Standard HTTP caching |
| Security | WS-Security at the message level | TLS plus tokens such as OAuth |
Choose REST for most web and mobile APIs, where lighter payloads and HTTP caching matter. SOAP still fits enterprise systems that need a formal contract or message-level security, such as older banking and insurance integrations.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
What is HATEOAS and why is it important?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
HATEOAS (Hypermedia as the Engine of Application State) means that API responses should include links to related actions or resources. This makes APIs self-discoverable and reduces client-server coupling.
Example response with HATEOAS:
{
  "id": 123,
  "name": "John Doe",
  "email": "john@example.com",
  "_links": {
    "self": "/users/123",
    "orders": "/users/123/orders",
    "edit": "/users/123",
    "delete": "/users/123"
  }
}
Benefits include improved API discoverability, reduced documentation needs, and easier API evolution.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
When would you use PATCH vs PUT?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Use PUT to replace a whole resource and PATCH for a partial update. With PUT, the body is the complete new version, so any field you omit should be reset to its default or null. With PATCH, the body carries only the fields to change.
PUT /users/123
{
  "name": "John Doe",
  "email": "john@example.com"
}
# Replaces entire user object

PATCH /users/123
{
  "email": "newemail@example.com"
}
# Only updates email field
PUT is idempotent, so a client can safely retry it. PATCH isn't guaranteed to be, because a patch such as "append an item" changes the result each time it runs. PATCH also sends less data. A PUT built from a stale copy can overwrite a field someone else just changed, so pair it with an ETag and an If-Match check.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
Explain idempotency in API design.
Compare different API authentication methods.
How would you implement role-based access control (RBAC) in an API?
What are the different API versioning strategies?
When should you introduce a new API version?
How should you structure error responses in APIs?
How do you implement pagination in APIs?
What caching strategies can you apply to APIs?
How do you implement rate limiting in APIs?
What are common API security vulnerabilities?
How do you secure API endpoints?
How do you implement API key management?
What is an API Gateway and when would you use one?
Explain the difference between synchronous and asynchronous APIs.
How do you design APIs for mobile applications?
What are webhooks and how do you implement them?
How do you handle file uploads in APIs?
Compare REST vs GraphQL APIs.
How do you handle API documentation and ensure it stays up-to-date?
How do you implement API analytics and usage tracking?
What are API design anti-patterns to avoid?
How do you implement API testing strategies?
How do you design filtering, sorting, and search on a collection endpoint?
How should an API client retry a failed request without making the outage worse?
How would you push real-time updates to API clients? Compare polling, long polling, Server-Sent Events, and WebSockets.
What is content negotiation in REST APIs?
What are HTTP response headers commonly used in REST APIs?
What are the differences between API-first and code-first approaches?
What are the security headers important for REST APIs?
How do you handle errors in gRPC?
What is gRPC metadata and how is it used?
What are gRPC interceptors and what are they used for?
How do timeouts and deadlines work in gRPC?
What is connection pooling in gRPC and how does it work?
How do you implement authentication in gRPC?
What are the different load balancing strategies in gRPC?
How do you handle streaming in gRPC?
What is gRPC health checking and how do you implement it?
How do you model a non-CRUD action, like cancelling an order, in a REST API?
How do retries work in gRPC, and which calls are safe to retry?
What is gRPC and when would you use it?
What are microservices and how do REST APIs fit into microservices architecture?
How do you handle backward compatibility in APIs?
How do you optimize API response times?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Measure first, then fix the slowest part of the request path. Track latency percentiles such as the 99th alongside error rates, because an average hides the slow tail users notice. Distributed tracing and APM tools show where each slow request spends its time.
The database is the usual bottleneck. Index the columns your queries filter and join on, and check slow queries with EXPLAIN. Fix N+1 queries, where a loop runs one query per item, with a join or one batched query. Connection pooling avoids a new connection per request. Read replicas spread read load, but they can lag, so reads that must see a fresh write go to the primary.
Caching skips the work. Keep hot data in Redis with a TTL, and clear it when the data changes. Send Cache-Control and ETag headers, so clients, CDNs and an API gateway can reuse responses. An unchanged resource then comes back as a bodiless 304 Not Modified.
Then shrink the response. Field selection lets a client ask only for what it needs, as in GET /users?fields=id,name,email. Compress responses with gzip, paginate long lists, and leave related resources out until the client asks for them.
Move heavy work off the request path. Async processing and background job queues let the API answer at once with 202 Accepted. Splitting into microservices helps scaling, not latency, because every remote call adds a network hop.
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How do you implement API monitoring and observability?
How do you design APIs for high availability?
What is API contract testing and how do you implement it?
What are the challenges of API deprecation and how do you manage them?
How do you design APIs for third-party integrations?
Answer it yourself first - out loud, or typed below.
How should your speech become text?
Listening… your words appear above as you speak - tap Stop when you're done.
Recording · cr - tap Stop & transcribe when you're done.
Transcribing with AI…
Voice:
Last attempt -
Treat the API as a product other companies build on, so stability and developer experience matter as much as features. Partners can't redeploy on your schedule, so a breaking change costs far more than in an internal API.
- Put developer experience first. Give partners clear documentation and an interactive API explorer. Add SDKs in popular languages and a sandbox environment.
- Pick an access model. Public APIs are open to all developers, partner APIs have restricted access, and private APIs are for internal use.
- Make onboarding self-service. Partners register and manage their own API keys. They pick a usage tier with billing, and know which support channels to use.
Offer the integration patterns partners expect. Webhook notifications and polling endpoints cover most needs. Add real-time APIs over WebSockets for live data and batch processing APIs for bulk work. Partners subscribe to webhook events through an endpoint like this one.
POST /partners/webhooks
Authorization: Bearer partner_token
{
  "url": "https://partner.com/webhook",
  "events": ["order.created", "order.updated"],
  "secret": "webhook_secret"
}
This answer doesn't lend itself to a diagram - it reads best . No credits were charged.
Why there's no diagram: “”
The interactive diagram is below the answer - jump to diagram ↓ · Below it, the related concept . Jump to it ↓
How do you handle data consistency in distributed API systems?
What strategies do you use for API performance testing?
How do you implement microservices communication patterns?
How do you design APIs for scalability?
How do you design a multi-tenant API so one tenant can never read another tenant's data?
Walk through the OAuth 2.0 authorization code flow with PKCE, and explain when you would use it.
How would you design a REST API for a complex domain with relationships?
What is the difference between API orchestration and choreography?
What are API gateways and service mesh, and how do they differ?
How do you optimize gRPC performance for high-throughput scenarios?
What is gRPC reflection and when would you use it?
How do you handle gRPC streaming backpressure?
How do you implement circuit breakers with gRPC?
How do you implement distributed tracing in gRPC?
What are the security best practices for gRPC in production?
How do you handle gRPC service discovery in a microservices architecture?
How do you implement graceful shutdown for gRPC servers?
How do you implement request validation in gRPC?
How do you debug and troubleshoot gRPC issues?
What is gRPC-Web and when would you use it?
How do you implement caching strategies with gRPC?
How do you handle versioning in gRPC services?
This answer is part of Pro.
The full written answer, with the trade-offs and follow-ups an interviewer will probe.
No matches
Try a different filter or search term.
The core concepts of API Design.
22 concepts in teaching order, one step-by-step diagram each. Go through one, then see every question it answers.
-
1
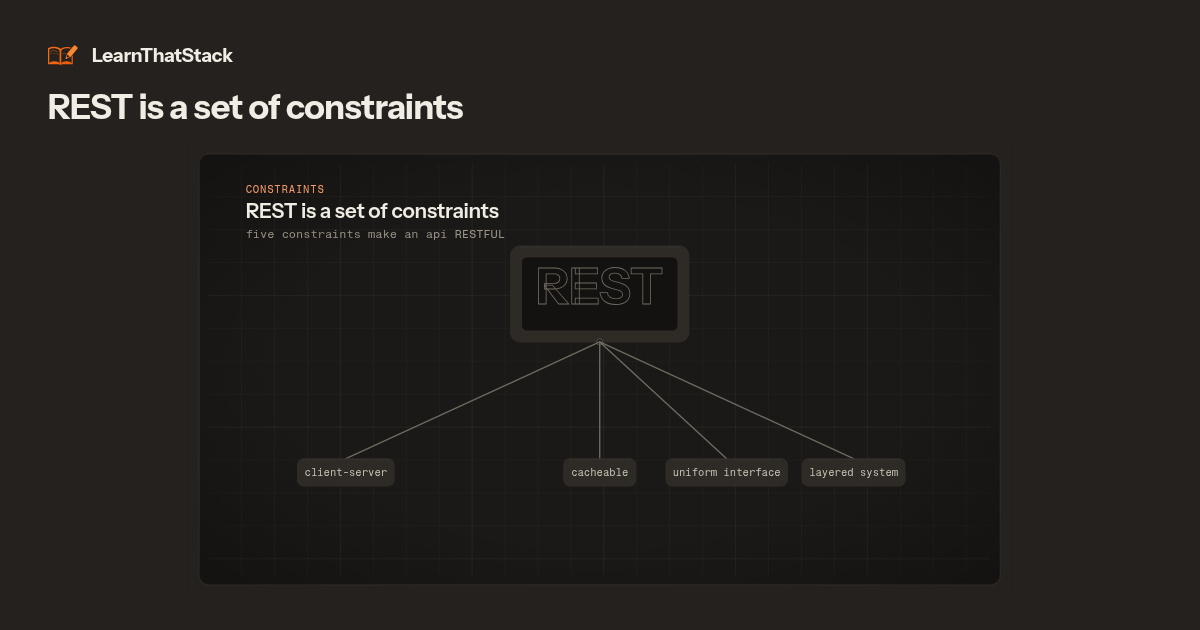 Thinking in resources: what REST actually is
REST is constraints, not JSON over HTTP: address resources, let methods decide the action, send hypermedia links to what's next and more.
Start →
-
2
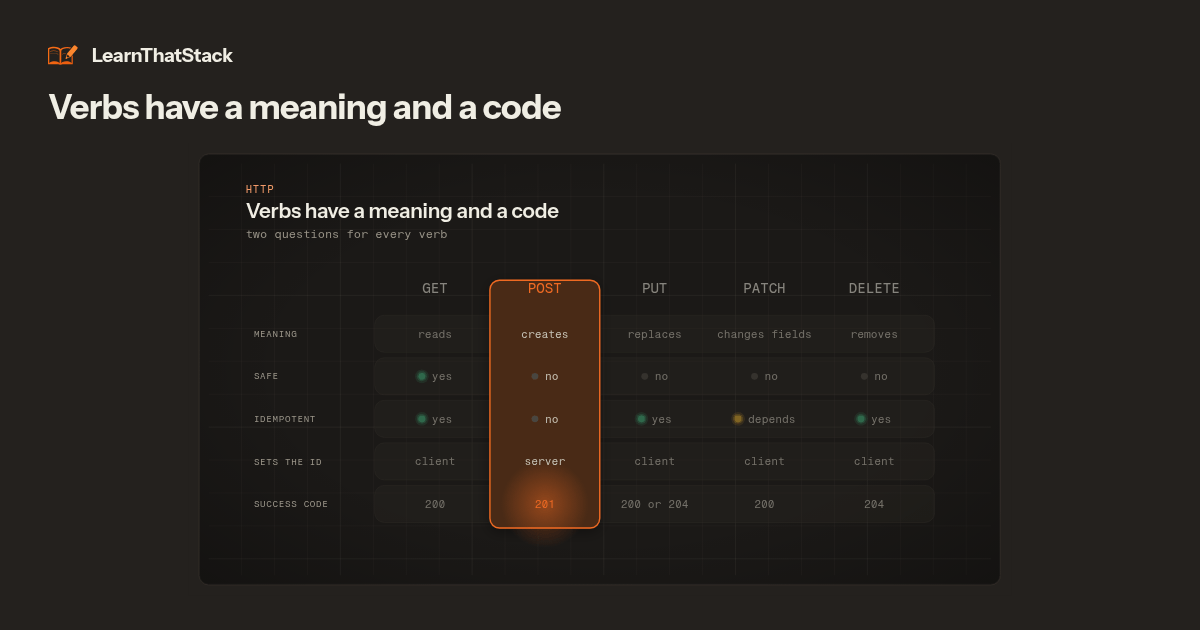 HTTP methods: what each verb promises
A method's promise about safety and idempotency decides when a retry is safe, when a cache is legal, and PUT versus POST.
Start →
-
3
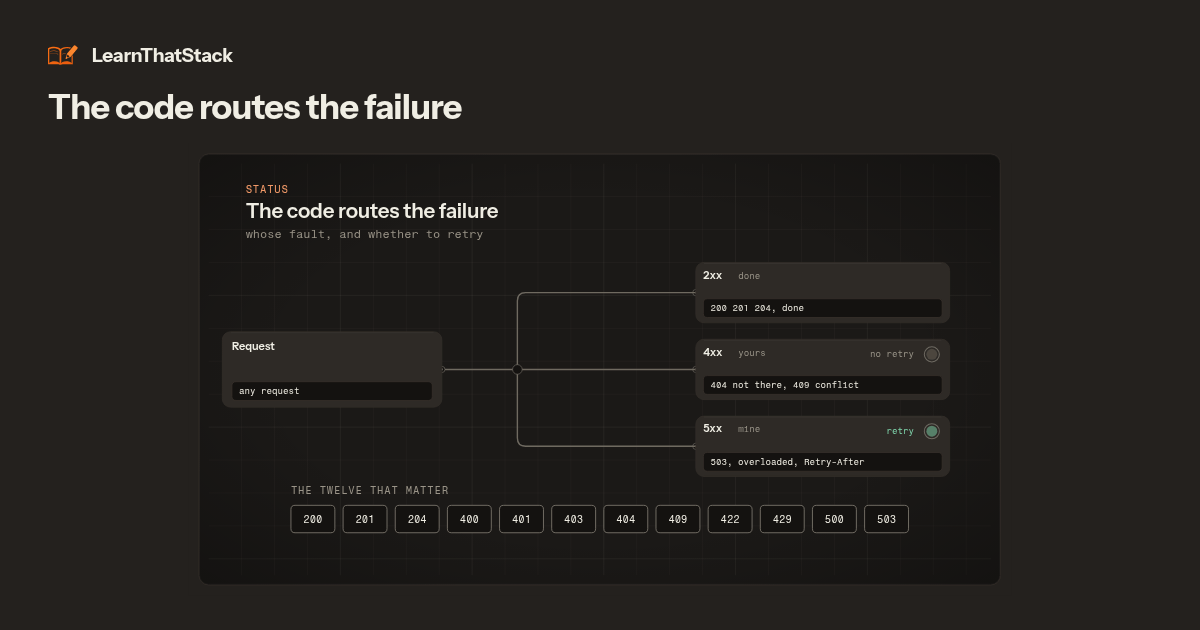 Status codes and error design: how an API says NO
The status code tells machines whose fault the failure was and whether to retry. The error body tells a developer what to fix, and it is never an apology.
Start →
-
4
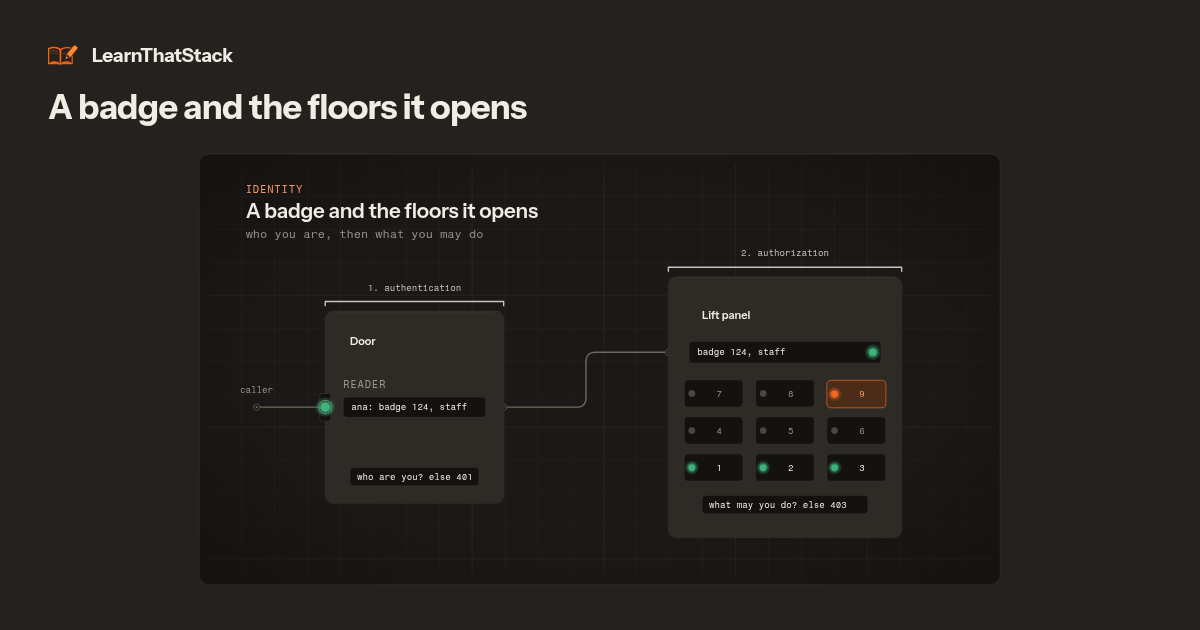 Authentication: proving who is calling
Authentication asks who you are and authorization asks what you may do. Authentication methods differ mainly in where the identity state lives.
Start →
-
5
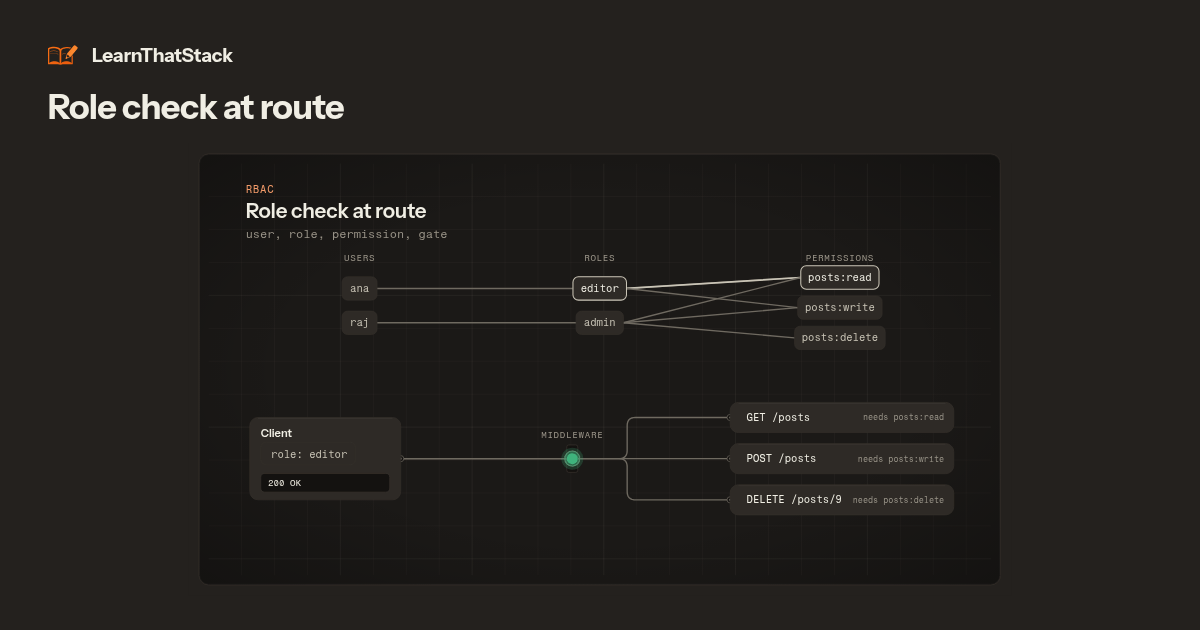 Authorization: a route check is not an object check
A role check at the route is needed but not enough. The most common API breach is never asking whether this user owns object 123.
Unlock →
-
6
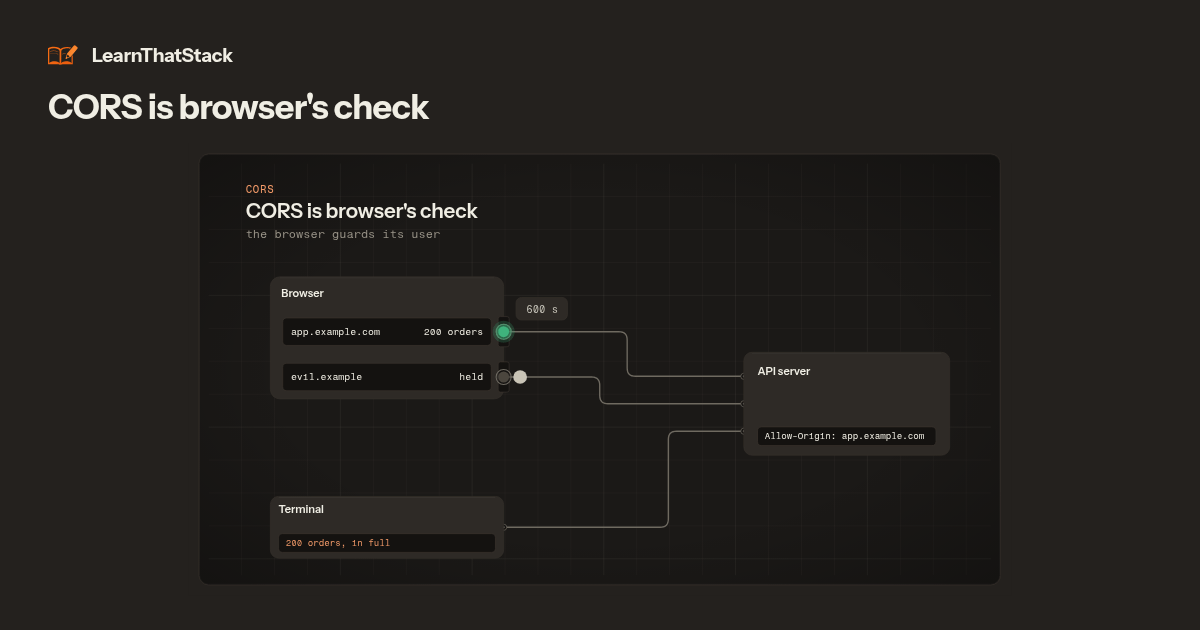 The browser enforces CORS, not your server
The browser runs the same-origin policy to protect its users. And CORS headers tell the browser which origins may read the reply, but requests from curl, POSTMAN don't go through that check.
Start →
-
7
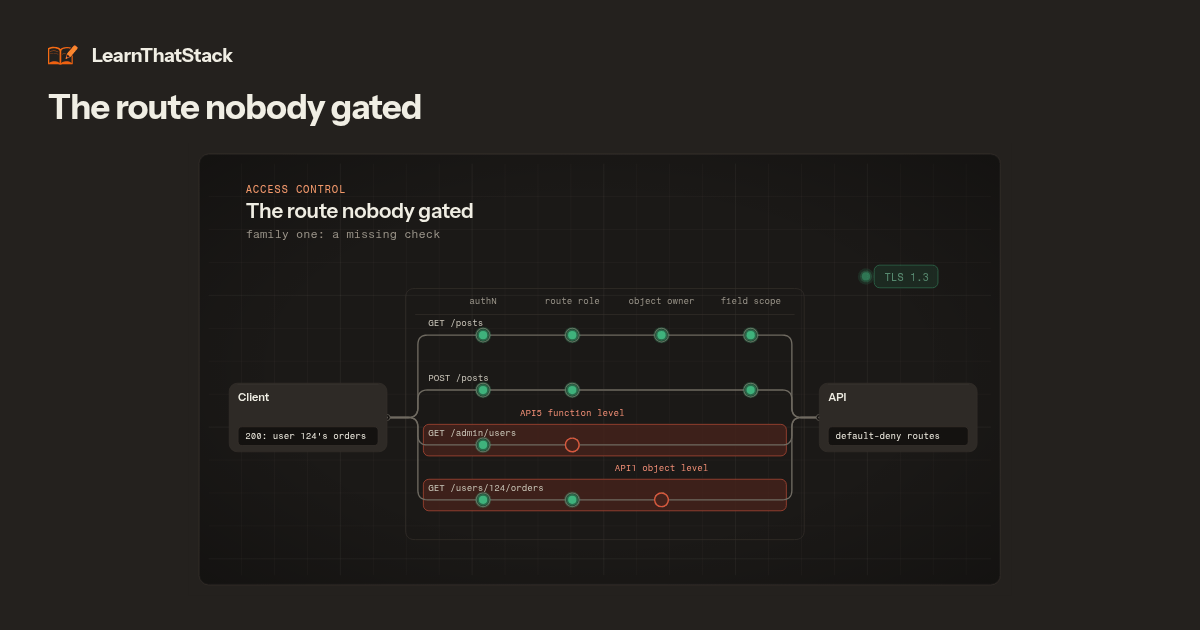 API security: three families of mistakes, not a top ten list
Real breaches come from missing checks, leaked fields and trusted input.
Start →
-
8
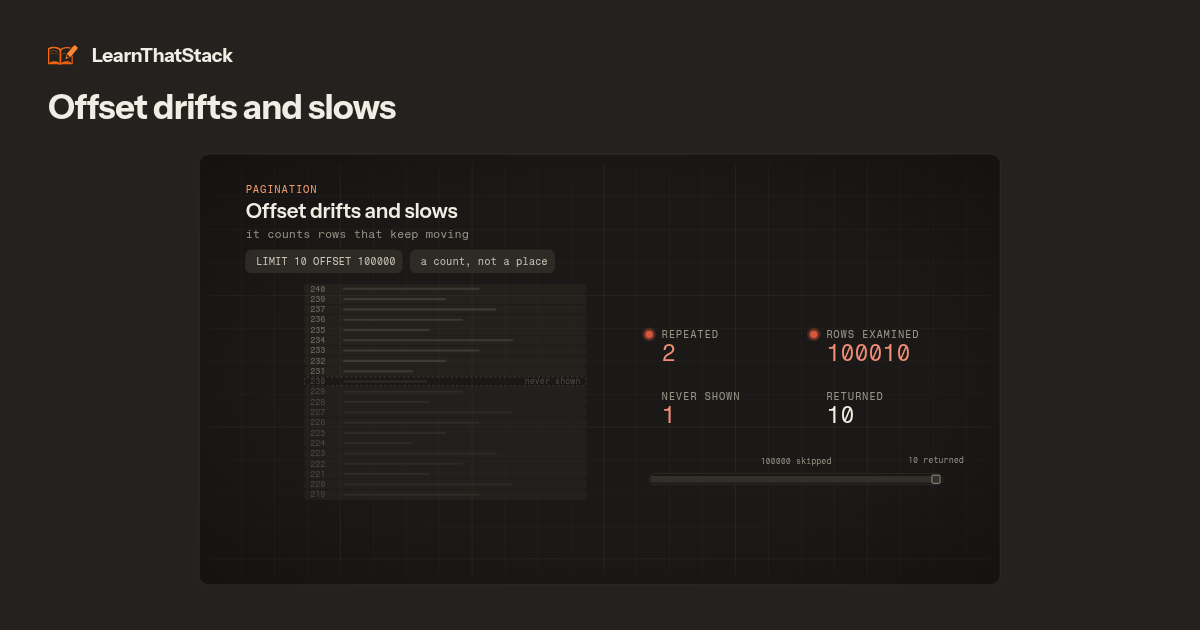 Designing a list endpoint is designing a small query language
Pagination, filtering, sorting and field selection are one problem. Offset paging drifts and slows down. A cursor pins your position to a stable key.
Unlock →
-
9
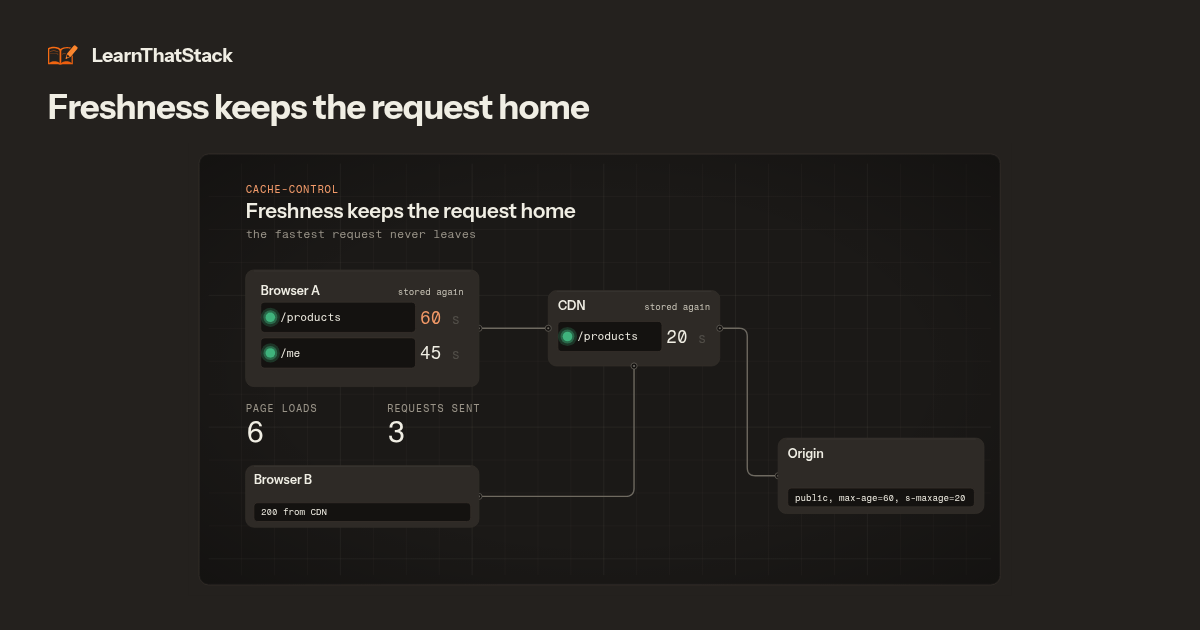 HTTP caching: infrastructure you do not own, working for you
Declare freshness with Cache-Control and identity with ETag, and caches serve your traffic. The hard part is invalidation.
Start →
-
10
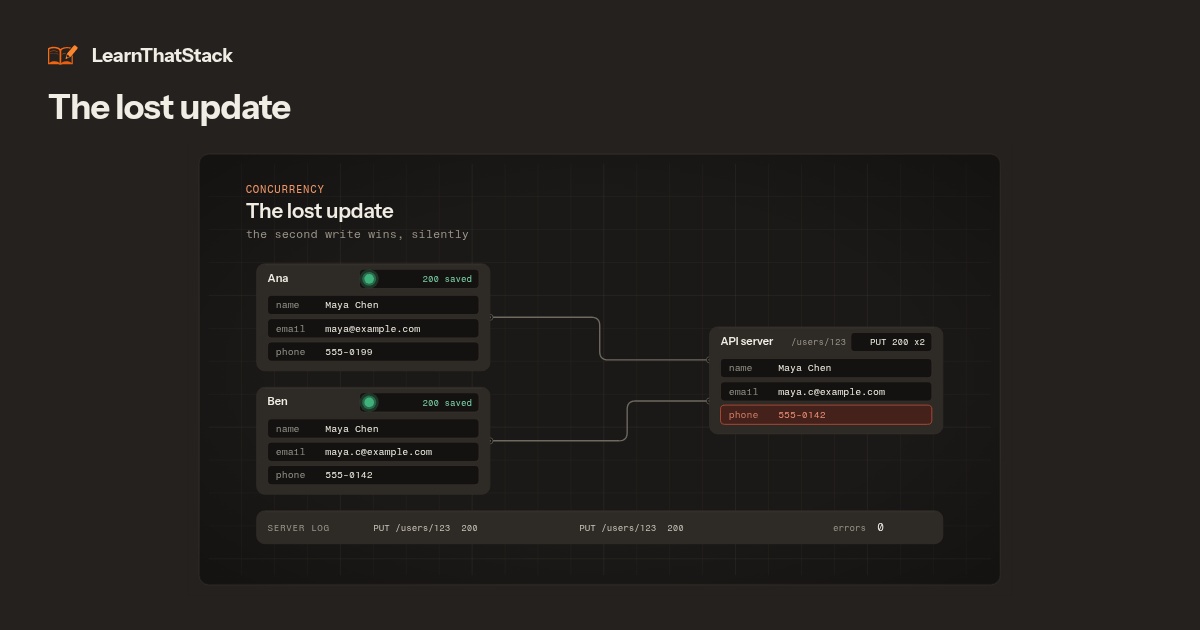 Conditional requests: the lost update and the fix HTTP already has
Two clients read one row and both write it back, and the slower write silently erases the faster one. If-Match makes that loss a loud 412.
Unlock →
-
11
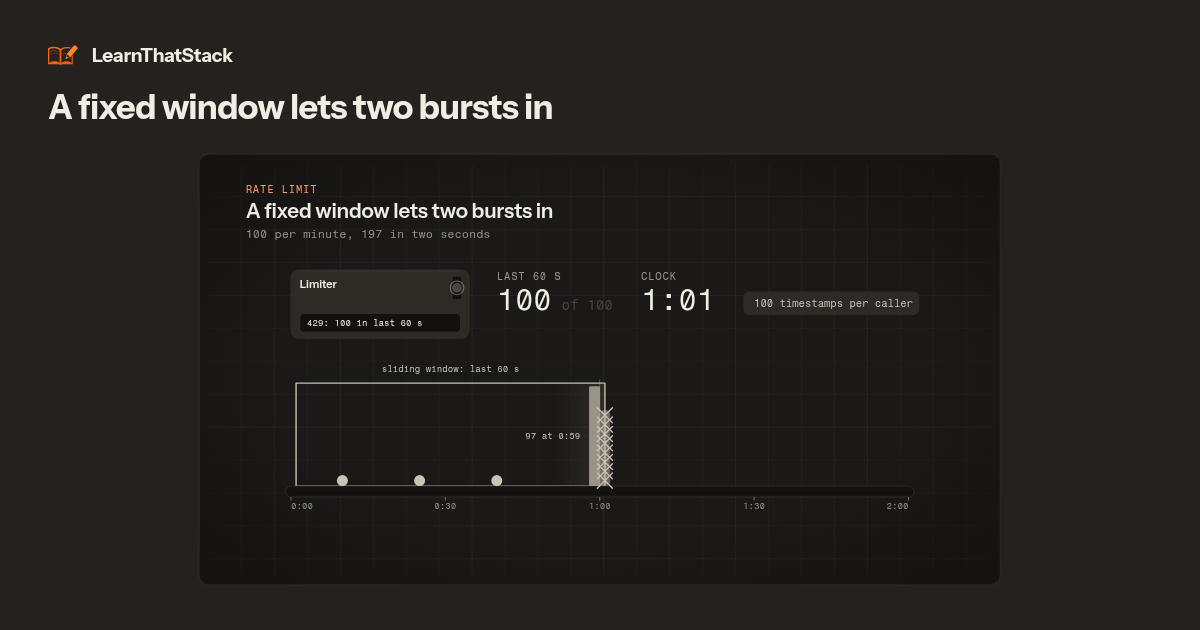 Rate limiting shares capacity fairly, and the algorithm decides how
A limiter protects a shared resource from any one caller, malicious or just retrying badly. The algorithm decides which bursts get through.
Start →
-
12
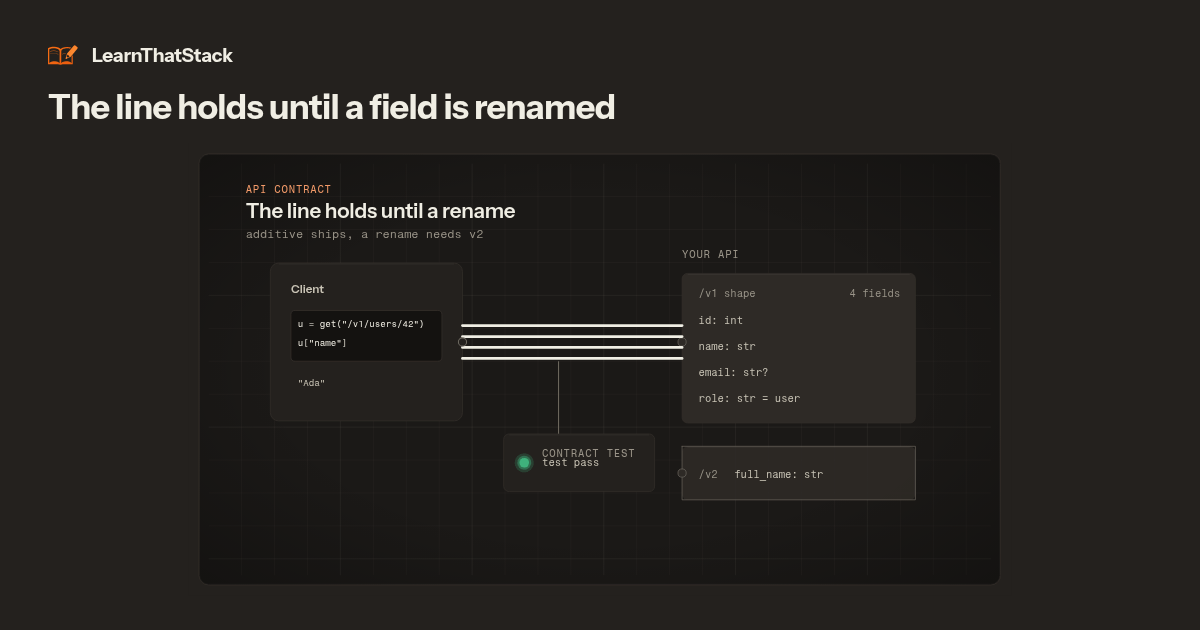 Versioning an API: changing the contract you already published
Only a breaking change needs a new version, and most changes are additive. The deprecation lifecycle matters far more than where the version number goes.
Start →
-
13
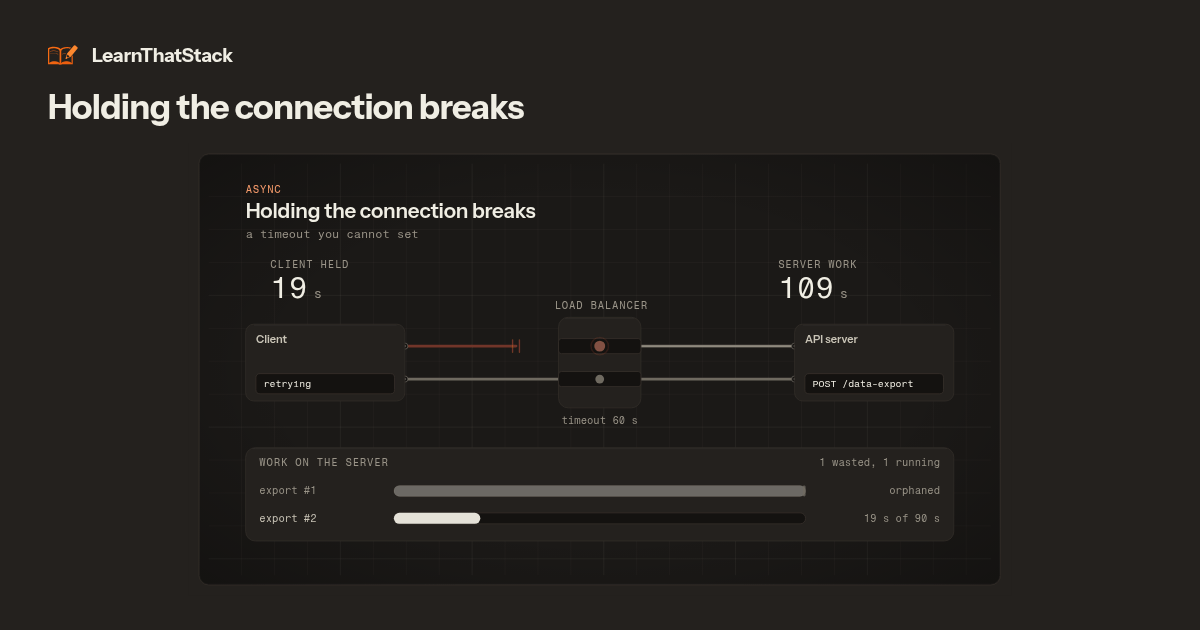 Async APIs and webhooks: when the work takes longer than the request
Do not keep the connection open. Return 202 with a job the client can poll, or send a webhook to whoever needs to know and handle every delivery problem.
Start →
-
14
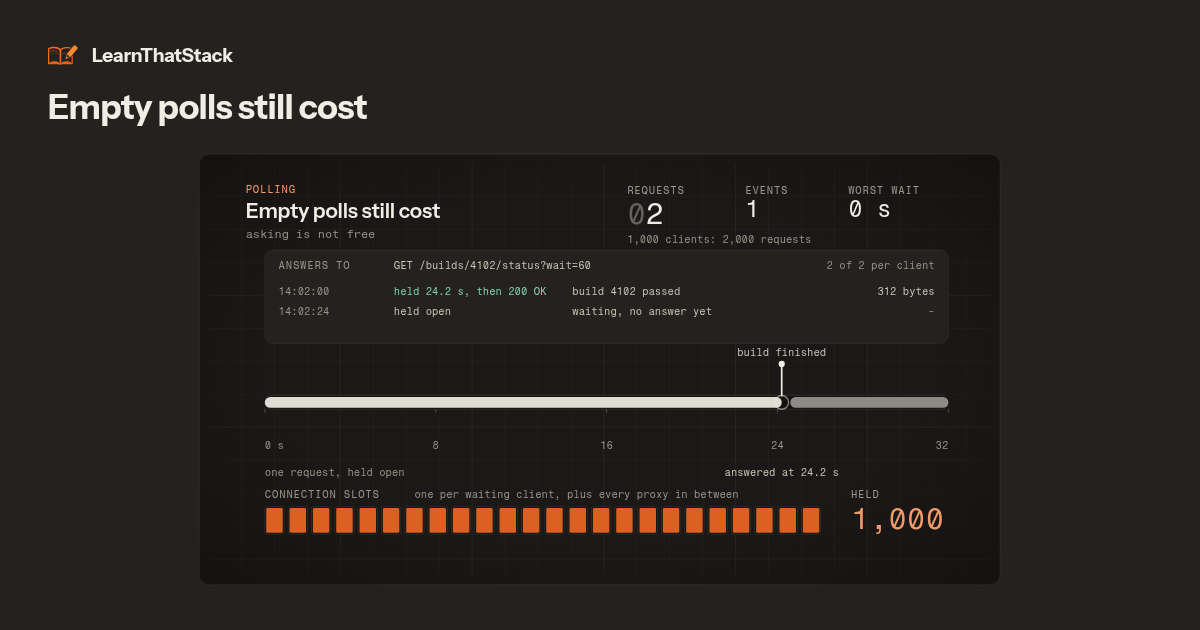 Real-time APIs: step up from polling only for a clear reason
Poll while the delay is acceptable. Push with SSE when only the server has new data, and open a WebSocket only when the client sends messages back.
Unlock →
-
15
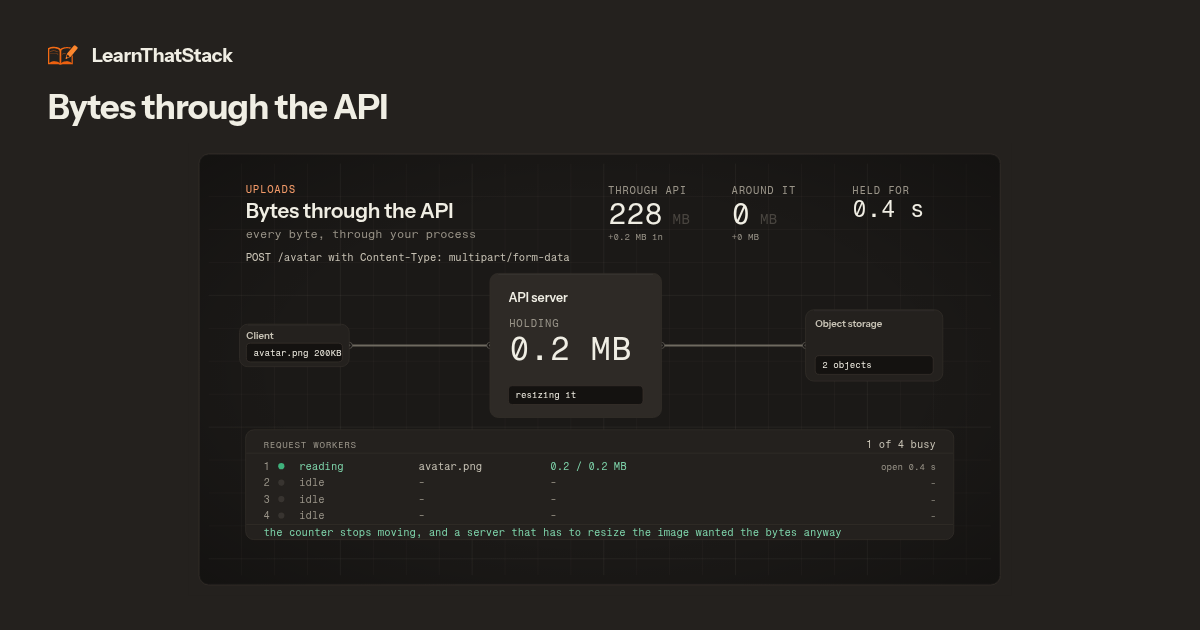 File uploads: do the bytes go through your API or skip it?
Every upload design makes one choice: the bytes go through your API or skip it. A signed URL gives permission to upload, but your API still keeps control.
Unlock →
-
16
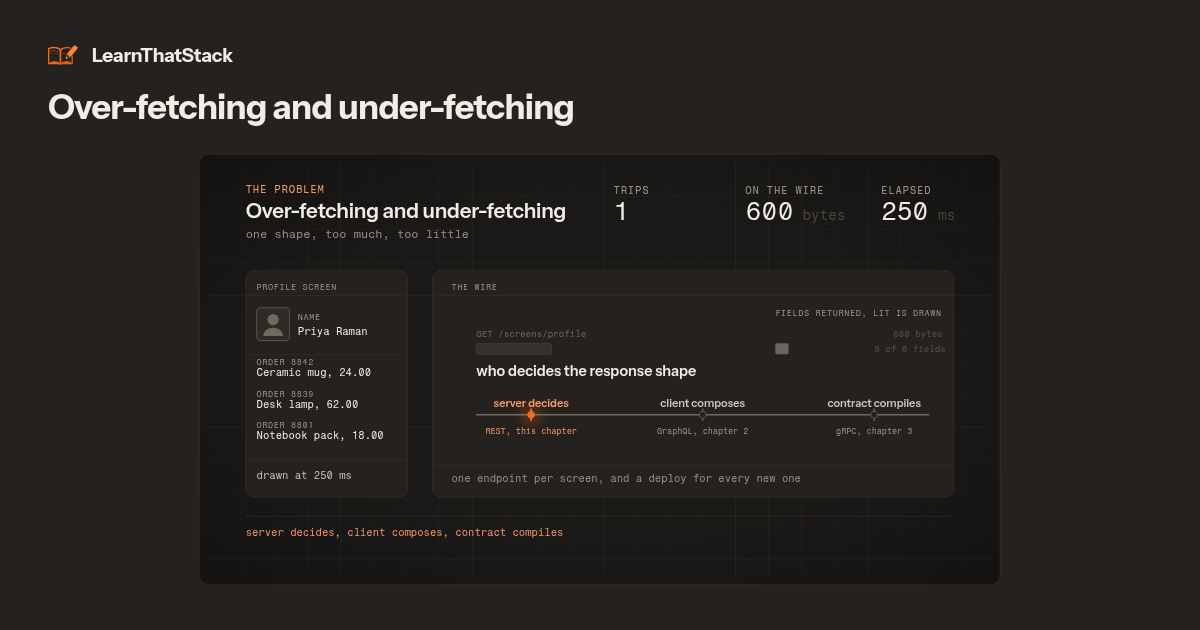 Who controls the response shape
In REST the server decides the response shape, in GraphQL the client builds it, and in gRPC a compiled contract sets it. The trade-offs come from who decides the shape.
Start →
-
17
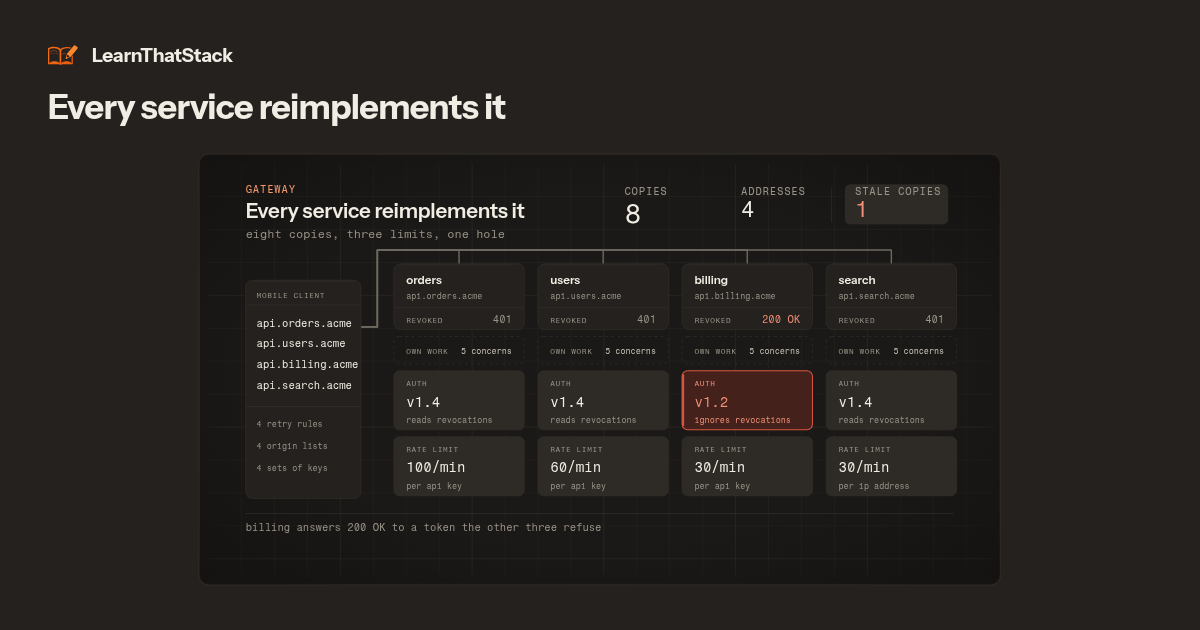 The API gateway: what belongs at the edge
A gateway exists so auth, rate limiting, routing and TLS are implemented once at the edge rather than copied into every service.
Unlock →
-
18
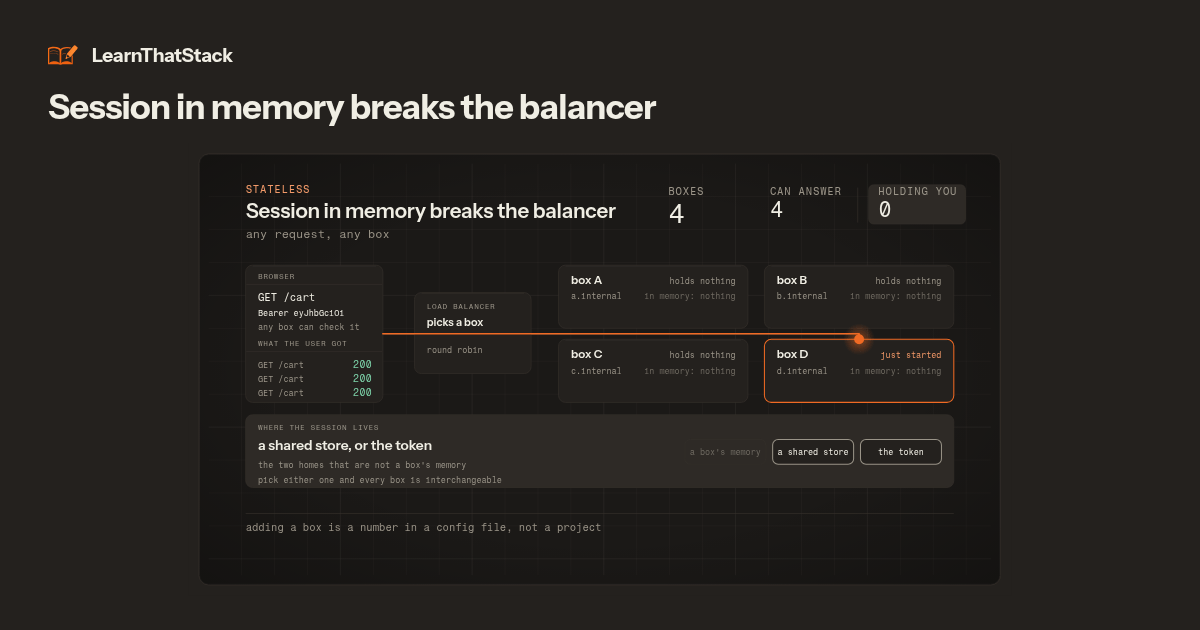 Scale and availability: what statelessness makes possible, and what still fails
Holding no session is what lets the servers scale out. For availability, the other half, assume parts fail and stop one failure from spreading.
Start →
-
19
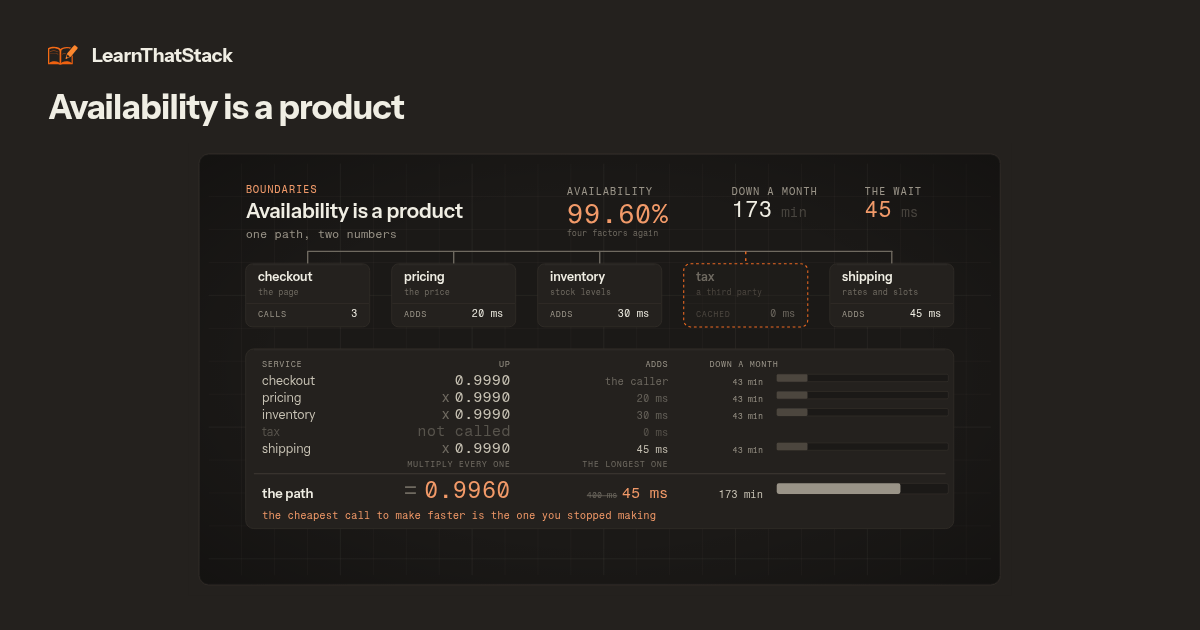 Service boundaries: chains, events, and sagas
Every call you add multiplies the risk. Events decouple services but data agrees later, and a saga replaces a transaction with compensations that undo earlier steps.
Unlock →
-
20
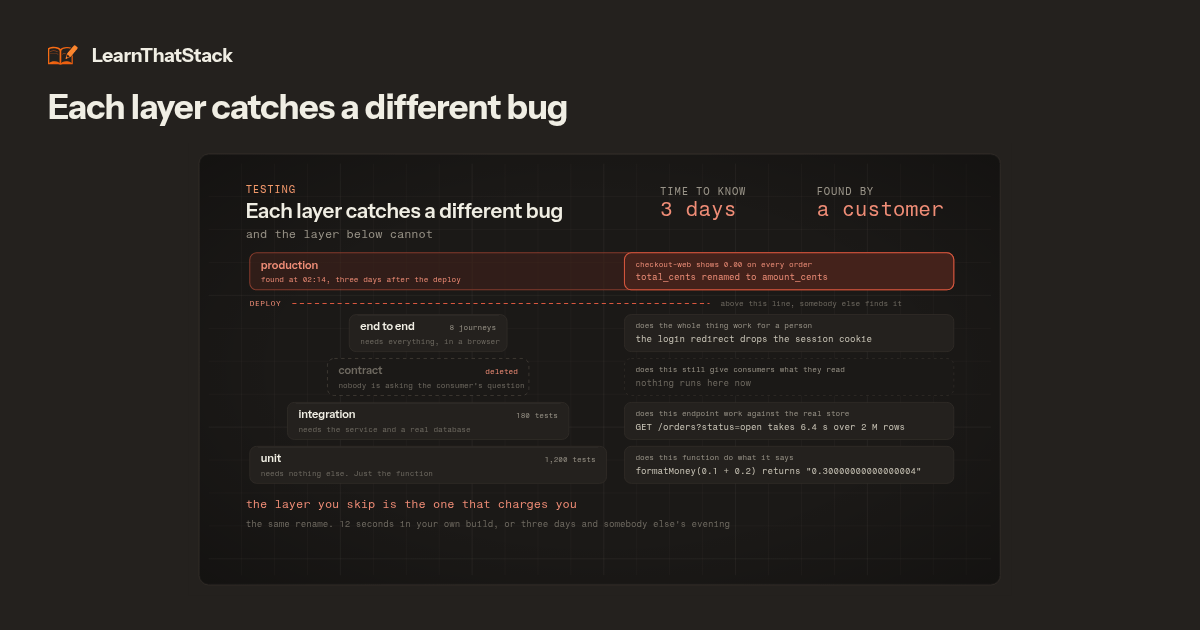 Testing APIs: three different questions
Three suites, three questions: behaviour, compatibility, capacity. The contract test is the one only an API needs.
Start →
-
21
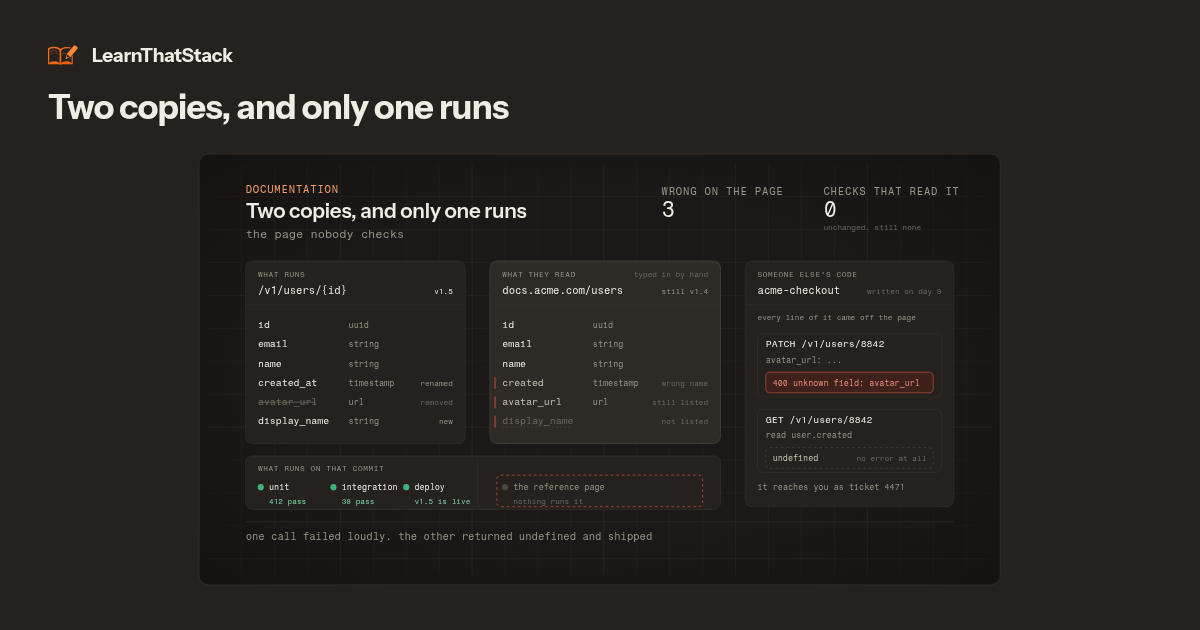 Documentation: the docs come from the spec, not a hand-written copy
Hand-written docs are a second copy of what the code does, and copies go out of date. A spec that generates the reference, clients and checks cannot go out of date.
Start →
-
22
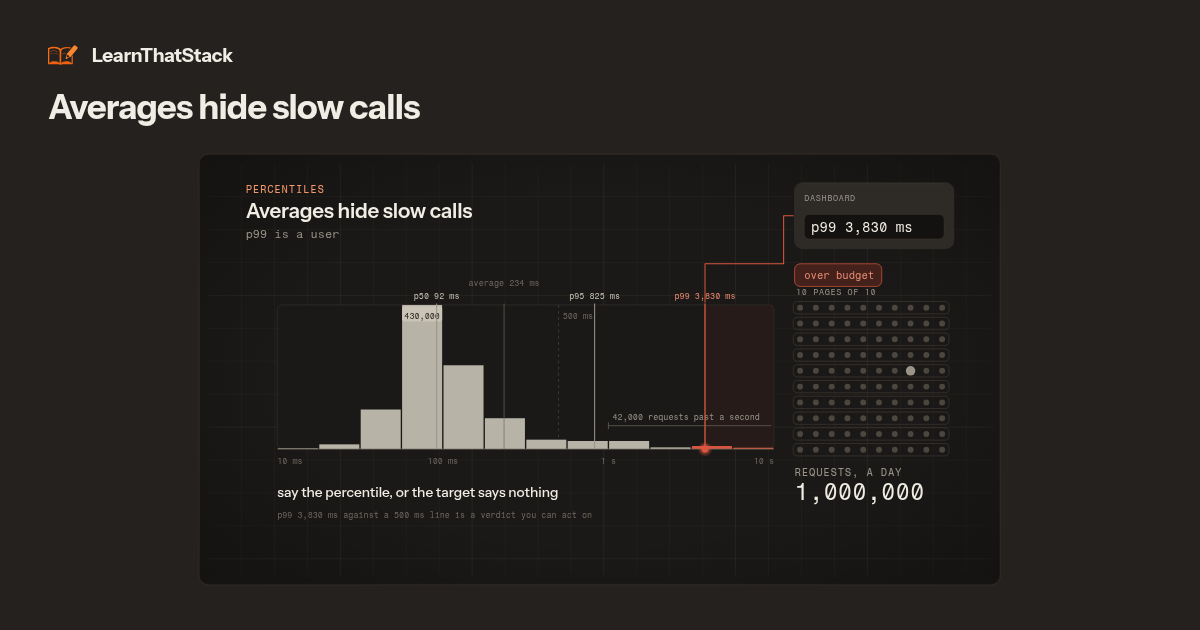 Observability: percentiles, one request id, and the signal that changes first
An average describes a request nobody made. A percentile describes real requests, one request id builds the trace, and saturation is the first signal to change.
Unlock →
API Design, in short videos.
API Design in pictures.
A quick recap of API Design in 36 short animated pictures, one idea at a time. About 9 min to get the whole topic back in your head before you walk in. Pause any picture, slow it down, or step through it.
Pro The first chapter is free to play. The other 32 pictures come with Pro.
API Design cheatsheet
- Resources & methods01
- Errors & retries02
- Auth & security03
- Paging, caching & speed04
- Versions & change05
- Async & real-time06
- Architecture & scale07
- gRPC basics08
- gRPC in production09
- Docs, tests & monitoring10
- The model11
- + 5 more inside

This picture is part of Pro. The first chapter is free to play; the other 32 pictures come with Pro.
Get Pro · $10/mo Already Pro? Sign in74 of 92 API Design answers are in Pro.
Full answers, code samples, and AI explanations that go simpler or deeper. Cancel anytime.
- Full answers + code
- AI explanations, simpler or deeper
- 1,000 AI credits / month
- Cancel anytime
Change topic
Pick a different technology or stack. Your current topic stays put until you choose a new one.
MEAN
MongoDB, Express, Angular, Node.jsMERN
MongoDB, Express, React, Node.jsDjango
Python Full-Stack DevelopmentRuby on Rails
Convention over ConfigurationServerless on AWS
Serverless Architecture on AWSInterviewers also test these - they're common to every stack, whichever one you picked above.
Flutter Mobile
Flutter Cross-Platform Mobile DevelopmentInterviewers also test these - they're common to every stack, whichever one you picked above.
Spring Boot
Enterprise Java Development.NET
Microsoft EcosystemVue
Vue.js, Vite, TypeScript, Tailwind, Node.jsGo Backend
Golang, gRPC, PostgreSQL, Redis, RabbitMQInterviewers also test these - they're common to every stack, whichever one you picked above.
FastAPI
Python, FastAPI, SQLAlchemy, PostgreSQLReact Native
React, TypeScript, Redux, FirebaseiOS Native
Swift, SwiftUI, UIKit, FirebaseAndroid Native
Java, Jetpack Compose, FirebaseDevOps / Platform
Docker, Kubernetes, Terraform, CI/CDInterviewers also test these - they're common to every stack, whichever one you picked above.
AI Engineer
LLMs, RAG, Agents, EvalsAI-Powered Developer
Claude Code, Copilot, Agentic WorkflowsCore SWE Interview Prep
Data structures, algorithms, OS, concurrency, networking, gitInterviewers also test these - they're common to every stack, whichever one you picked above.
Interviewers also test these - they're common to every stack, whichever one you picked above.